
From Frameworks to Containment
Operationalize NIST SP 800-207 and CISA ZTMM 2.0 with the Aviatrix Cloud Native Security Fabric (CNSF) — centralizing policy, encrypting traffic, and containing breach paths across clouds. Containment is the enforcement layer that makes Zero Trust operational.
Frameworks define “why”; clouds obscure “how.”
Zero Trust frameworks define intent—encrypt, verify, and limit privilege—but not enforcement. In multicloud environments, ephemeral workloads and IP-based policies create blind spots where lateral movement thrives.

Frameworks define intent — not enforcement
Zero Trust frameworks like NIST SP 800-207 and CISA ZTMM 2.0 define why to encrypt and verify but stop short of how to enforce those controls in the cloud. Organizations need enforcement built into the network fabric itself.

Ephemeral workloads break static controls
Dynamic workloads spin up and disappear in seconds, making IP-based policies and static firewalls obsolete. Without identity- or tag-based segmentation, Zero Trust boundaries collapse as environments scale.

Cloud networks lack built-in Policy Enforcement Points
Most networks still depend on centralized or perimeter controls instead of enforcing policy where workloads actually run. Without distributed PEPs, lateral movement and data exfiltration remain possible even in Zero Trust-aligned environments.
Aviatrix CNSF: The Implementation Layer for Zero Trust Frameworks
From Frameworks to Containment
Zero Trust frameworks define why — Aviatrix CNSF delivers the how. Built on NIST SP 800-207 and CISA ZTMM 2.0, CNSF provides a unified policy engine and distributed Policy Enforcement Points (PEPs) across every cloud. Identity-driven segmentation, FIPS-validated encryption, and per-session authorization contain breaches and prove maturity in runtime.
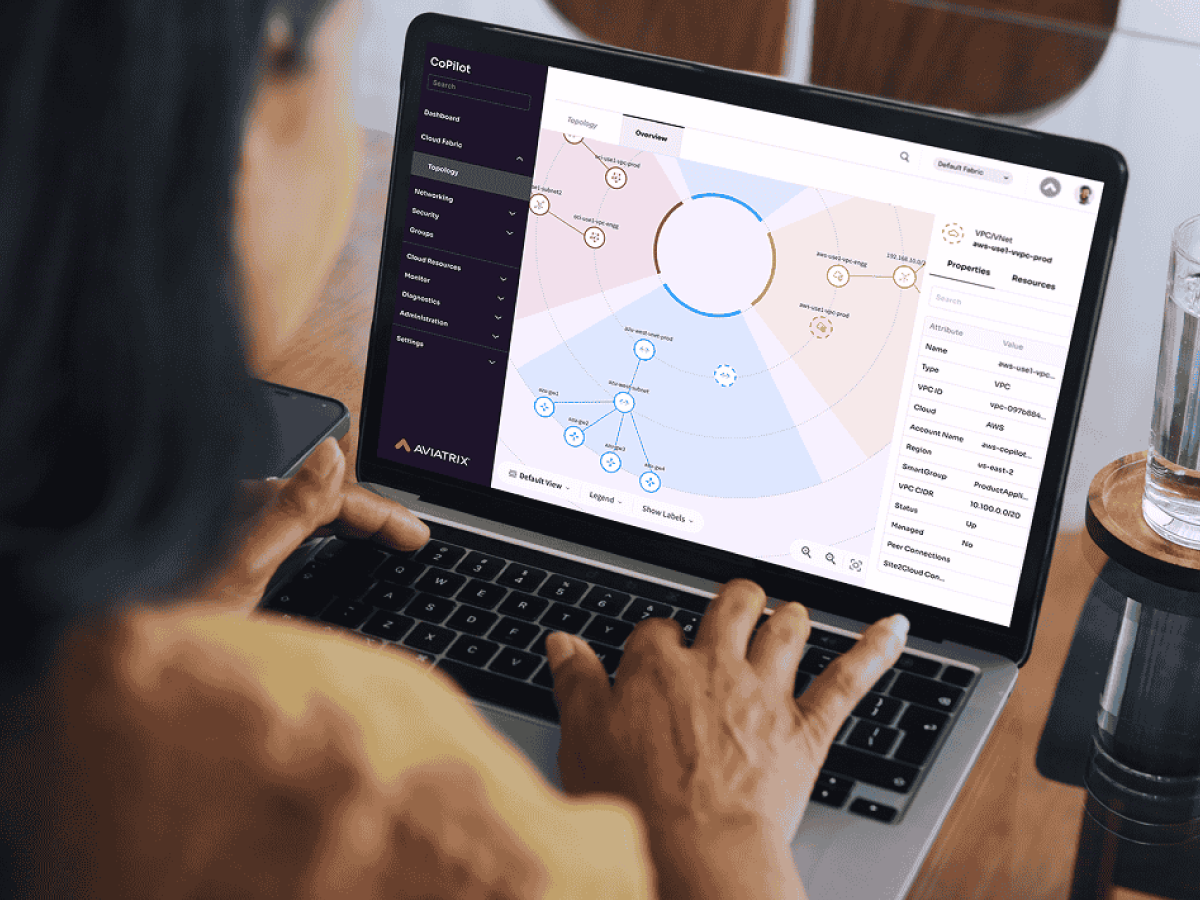
Architecture for the 'How'
A single control plane translates Zero Trust intent into native enforcement with continuous visibility and audit across AWS, Azure, and GCP.
Identity over IPs, runtime
SmartGroups use identity and tags—not IPs—to segment ephemeral workloads, keeping Zero Trust boundaries intact as apps launch and scale.
Policy Enforcement at Every Workload
Guided by NIST SP 800-207 and CISA ZTMM 2.0, Aviatrix CNSF places Zero Trust enforcement next to each workload with distributed PEPs that inspect, encrypt, and authorize every connection in runtime.
Aviatrix CNSF: Zero Trust Maturity Benefits
Identity-driven segmentation, FIPS-validated encryption, and continuous telemetry advance maturity across the Network, Workload, and Data pillars. Agentless automation simplifies operations while unified visibility secures VMs, containers, and AI workloads — reducing breach risk and proving Zero Trust readiness.
of data-in-transit encrypted
of network policies enforced at runtime
agentless enforcement
Schedule a Free, Attack Path Assessment
Sign up to see your cloud the way attackers do. With Aviatrix Workload Attack Path Assessment, validate defenses, strengthen segmentation, and advance zero trust readiness today.
Your inbox is safe. We respect your privacy. By submitting this form, you agree to ourprivacy policy.

Ready to Secure Your Workloads?
Discover Aviatrix Cloud Native Security Fabric (CNSF) for unified, embedded security in the cloud fabric.
