A recent report from Futuriom by Scott Raynovich, “Implementing Crypto-agility for PQC Networking Infrastructure,” addresses the looming threat of Q-Day with practical recommendations for prioritizing crypto agility in enterprise networking infrastructures.
The report, commissioned by Aviatrix, addresses the challenges of data longevity, complex and aging infrastructures, and why enterprises need to address the danger of the Harvest Now, Decrypt Later strategy that adversaries are using today.
Q-Day: A Future Reality with Current Implications
Q-Day is the day when quantum computers have developed enough to break public-key encryption. While no one knows what the actual date will be, threat actors can intercept encrypted traffic today and store it until they can decrypt it. This practice is called Harvest Now, Decrypt Later.
NIST has released new post-quantum cryptographic standards, but those standards may change later. The report emphasizes the value of achieving a resilient infrastructure through crypto agility, not a simple algorithm update.
Assessing the Risk: AI Infrastructure and Data Longevity
In the report, Scott calls out two challenges for enterprises:
AI infrastructure that is distributed and crosses many regions and domains, requiring a secure overlay
Data that stays valuable even years after it’s stolen
The first challenge means that enterprises need to secure the whole network: the entire set of pathways data can travel. The second means that Harvest Now, Decrypt Later puts data in transit at risk.
Distributed infrastructures and data longevity mean that a post-quantum cryptographic transition is not a simple, one-time update. Instead, a full transition will require inventorying assets with deep visibility across a network to find what workloads are the most vulnerable.
Government Mandates as a Reference Point
Governments have responded to the threat of Harvest Now, Decrypt Later with mandates like Executive Orders 14412 and 14413 and the Office of Management and Budget’s memorandum M-26-15 that set timelines for planning and migrating to post-quantum cryptographic standards. The report details each mandate, its requirements, and its timeline.
The closest deadline is October 22, 2026, the date when civilian agencies must submit PQC migration plans according to OMB M-26-15.
While enterprises need to align their migrations with these standards, they are part of a larger issue. "There’s more to it than government mandates—it’s about building a secure, resilient infrastructure that can secure data and networks across any domain, including traditional enterprise, cloud, and telecom networks," Scott Raynovich explained.
Learning from the Major Cloud Service Providers
Scott details how major infrastructure providers are transitioning to quantum-safe algorithms. Google, Microsoft, Cisco, and Cloudflare each use PQC algorithms in some way, but they each cover their own services, not their customers’ entire networks. Each enterprise must own its own post-quantum compliance across its estate.
PQC for Infrastructure Architects: Mythos and Patching
The report brings up Mythos, the Anthropic model that demonstrated LLMs’ ability to discover and exploit vulnerabilities faster than defenders can patch them. Mythos has kicked off a network refresh, which is helpful as enterprises need to migrate to post-quantum cryptography. However, a hardware refresh will not cover all the traffic in a hybrid or multicloud network, such as cross-cloud or east-west traffic.
Rather than choosing between hardware and software as the solution, Scott recommends that enterprises “extend quantum-ready capabilities from the refreshed devices into the software-defined cloud network.” He describes seven elements for making a multicloud network crypto-agile, including encrypting data in motion at network speed and using segmentation to bound exposure.
Aviatrix Harvest and Decrypt Protection
The Futuriom report profiles Aviatrix Harvest and Decrypt Protection, which defends organizations against Harvest Now, Decrypt Later through crypto-agile encryption and Communication Governance. The offer rests on four technology pillars: Encryption, Egress Governance, Segmentation, and Crypto Agility.
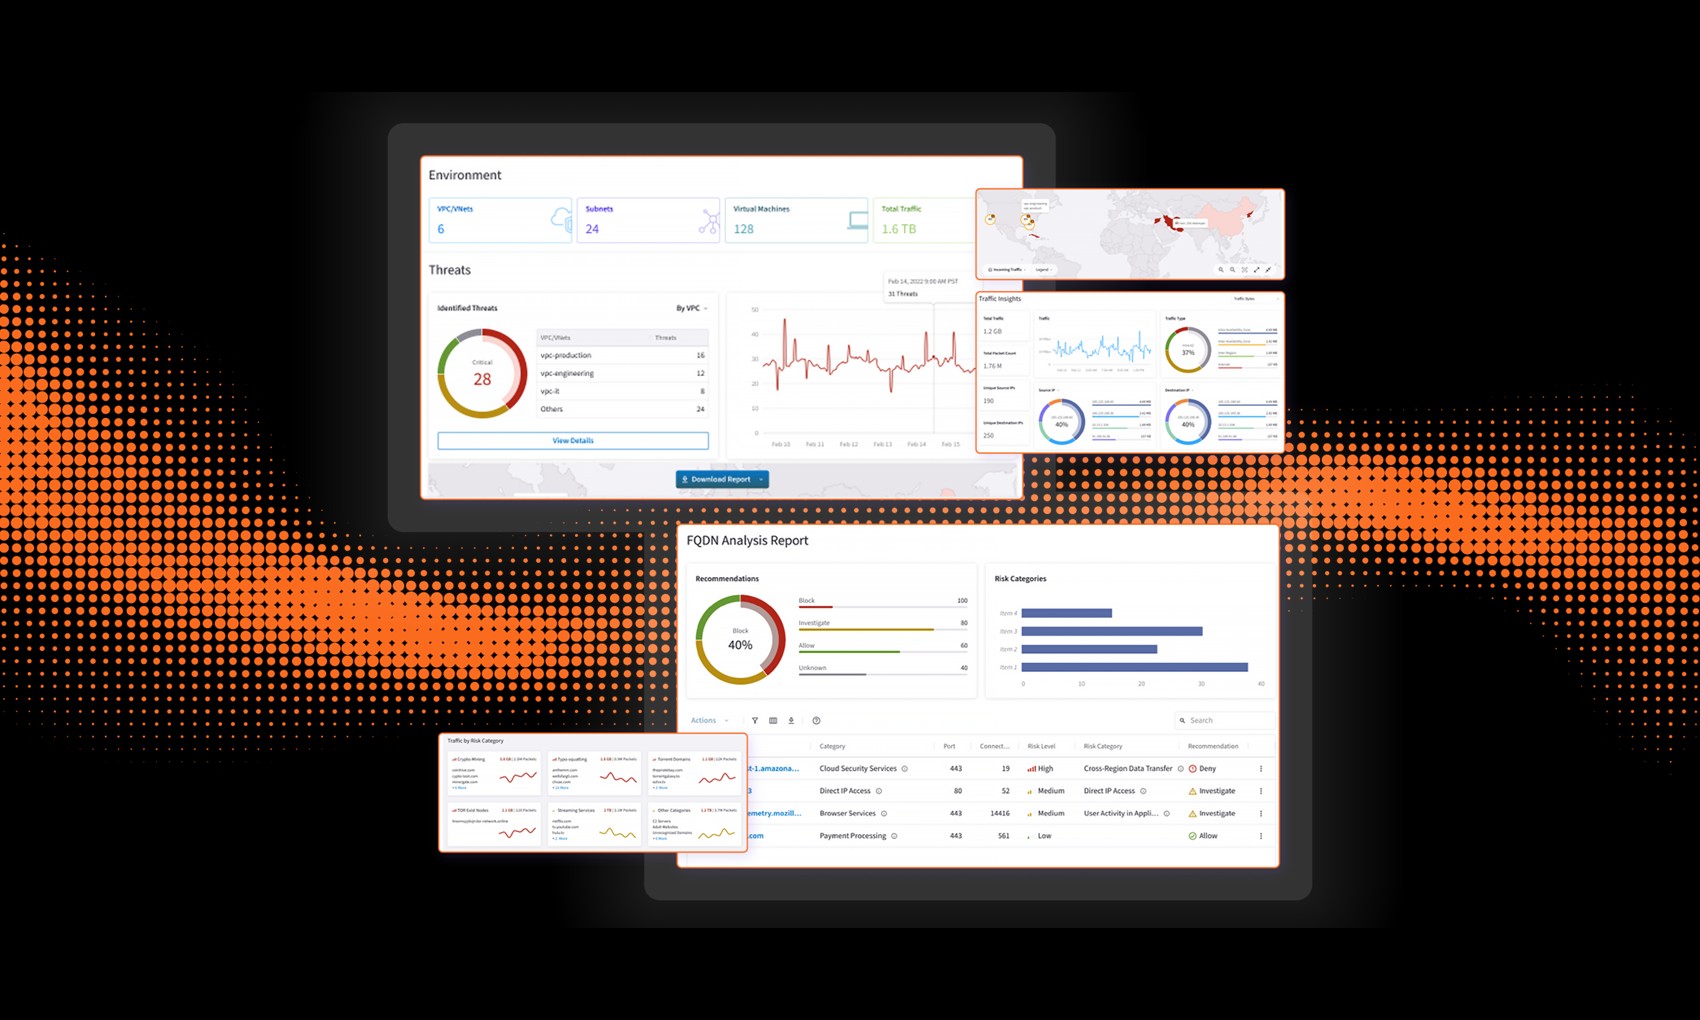
This solution meets the seven named requirements for crypto agility through products like Aviatrix’s patented High Performance Encryption and identity-based security policies. It provides deep visibility and helps organizations build a full cryptographic inventory with a free, two-phase Containment Assessment that reveals containment gaps and harvest exposure. Harvest and Decrypt Protection makes Aviatrix Cloud Native Security Fabric quantum safe.
Key Takeaway: Building Crypto Agility
The Futuriom report identifies two short-term goals that are more important than correctly guessing the date of Q-day:
Reducing how much long-lived data is available for Harvest Now, Decrypt Later exfiltration
Decreasing the time needed for a network transition when standards change
A migration to post-quantum cryptography should be integrated with network modernization itself. The best posture for a network now is crypto agility: the resilience needed to adapt quickly to whatever encryption or security challenges come next, Q-Day included.
This research brief is sponsored by Aviatrix. The analysis and conclusions are Futuriom's independent assessment; an included solution profile describes the sponsor's offering.
Ready to see Aviatrix in action?
Get a personalized live demo walkthrough or explore our latest deep-dive cloud threat research intelligence.
Gartner Strategic Roadmap for Zero Trust Security Programs 2025 Report
Download and gain actionable insights to advance your cloud security strategy.