
Containment for Every Workload
Extend Zero Trust into the runtime layer of the cloud, where modern applications, AI agents, and serverless functions operate. Containment — enforcement at every workload, on every path, independent of detection — is what runtime security must deliver.
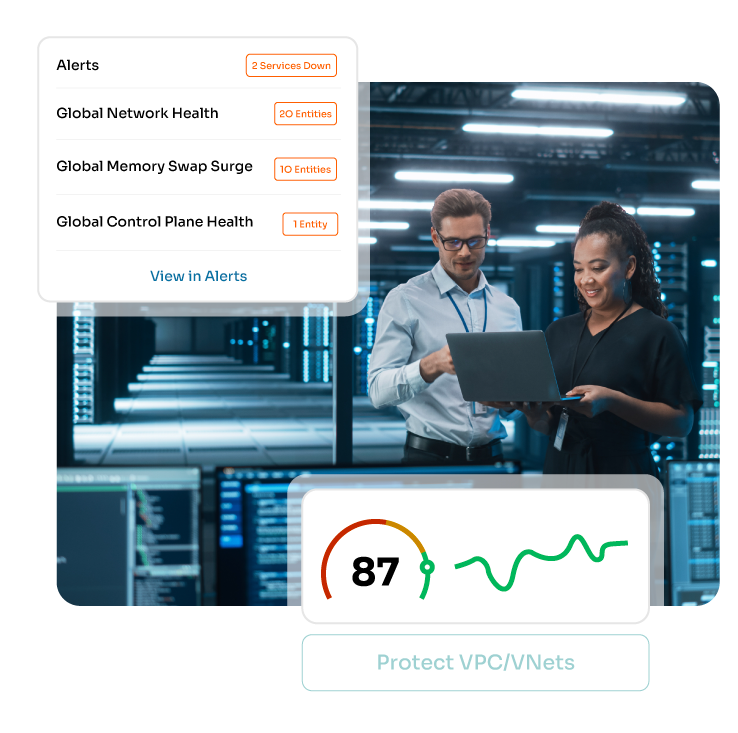
The Challenge: Zero Trust Stops at the Perimeter
Traditional Zero Trust implementations focus on user access, not workload communication. Your cloud defenses have critical blind spots that allow attackers to move without runtime enforcement or visibility.

Native controls don’t scale
AWS, Azure, and GCP each offer their own siloed firewalls, but none provide consistent visibility across clouds.

Runtime visibility is missing
Perimeter tools monitor egress traffic, but not live workload traffic flows in the cloud.

Zero trust maturity gaps
Security teams need runtime evidence that controls are reducing blast radius and data loss, not just static snapshots.
Zero Trust Enforcement for Every Workload Across Every Cloud
The Solution: Aviatrix Zero Trust for Workloads
Powered by Aviatrix Cloud Native Security Fabric ™ (CNSF) platform, the Zero Trust for Workloads product suite delivers pervasive, agentless zero trust controls that adapt to dynamic environments such as Kubernetes, serverless, and AI-driven applications.

Are your workloads fully secure? Find out today.
Uncover unencrypted traffic and hidden risks with a free assessment; leverage CNSF to reduce cost, risk, and complexity.
