
Building Security Programs Under Fire
In the latest episode of "In Progress," Aviatrix CEO Doug Merritt sits down with Aviatrix CISO John Qian to trace his unlikely journey from product engineer to security leader, unpack what it took to build Zoom's security program in the middle of a pandemic, and explore why AI is rewriting the rules on both sides of the fight — and why none of it matters if you haven't thought about containment.
Stay in the Loop
Get exclusive access to the latest conversations with cloud leaders, industry pioneers, and technology changemakers.
Subscribe and stay ahead of what's next.
Zero spam. Unsubscribe at any time.
Key Summary
- Security expertise doesn't come from building security products. John's career pivot began when customers started finding vulnerabilities in Cisco's own tools — and his team couldn't explain how the attacks worked.
- Building security at hypergrowth means flying while you build. John grew Zoom's security team from 10 to 300 during COVID, pausing all development to fix security bugs while fending off nation-state attackers.
- Shift-left only works if you show up prepared. Run risk assessments early, join design meetings for high-risk features, and tune CI/CD tooling carefully — false positives destroy credibility with developers.
- AI makes design reviews more comprehensive than any human. It can also generate proof-of-concept exploits in minutes instead of days, which means attackers have that same advantage.
- Think containment by default, not just patch and pray. With AI accelerating vulnerability discovery and supply chain attacks putting compromised workloads directly into your environment, the vulnerability deficit means patching alone will never be enough.
The Speaker
Doug Merritt spent seven years leading Splunk, the company that defined the detection era of cybersecurity, growing annual recurring revenue from $220 million to $3.12 billion. As Chairman, President, and CEO of Aviatrix, he now makes the case that detection is no longer enough. He has expanded the multicloud networking leader into Zero Trust protection for cloud networks and workloads, and in 2026 declared the arrival of the Containment Era, built on a simple thesis. Trust will be violated. The only question is whether your architecture bounds the blast radius when it is. Earlier, he held senior leadership roles at Cisco, SAP, and PeopleSoft.
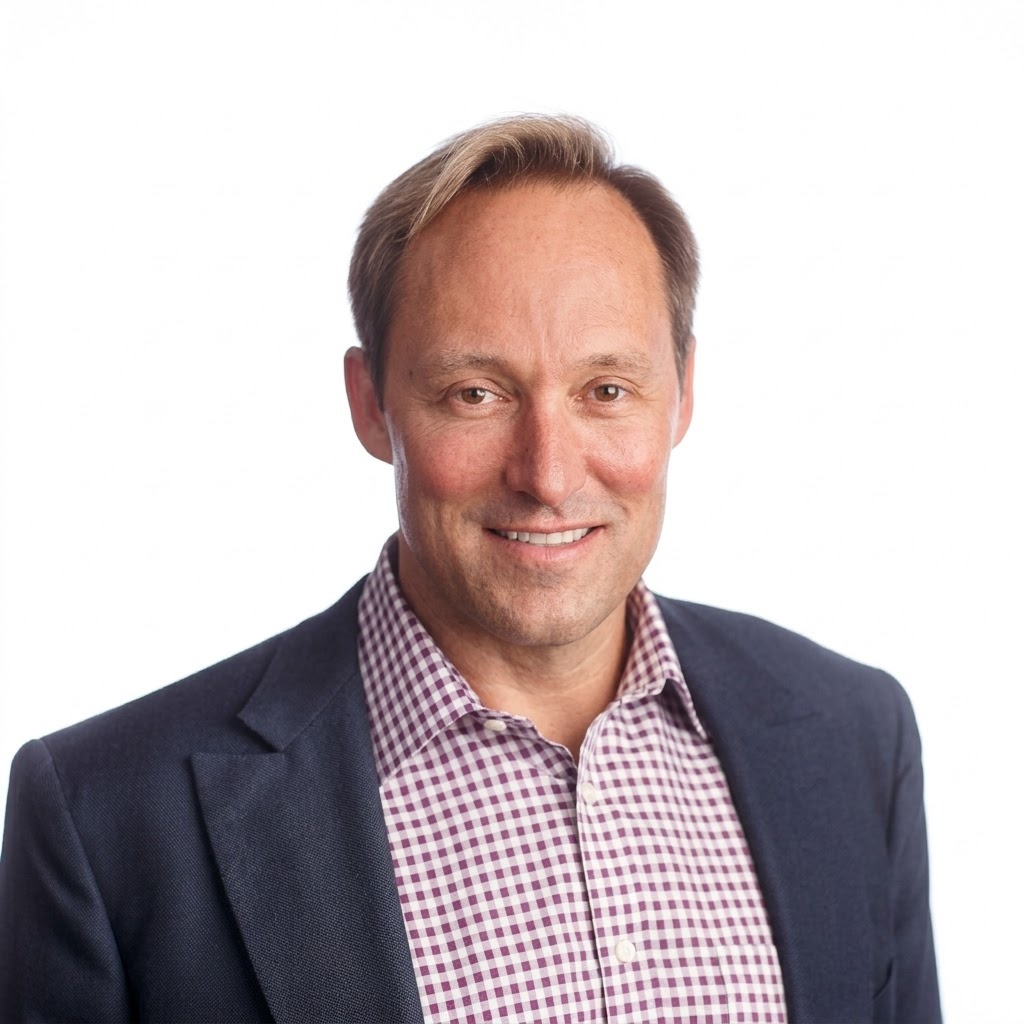
Doug Merritt
The Guest
John is the Chief Information Security Officer at Aviatrix. Previously, he served as Head of Security Architecture at Zoom, where he oversaw the security posture of Zoom's products, cloud environments, and sensitive IT applications. Over four years, his team built one of the industry's most mature security programs while supporting Zoom's dramatic growth during the pandemic.
Before Zoom, John was a Principal Engineer at Cisco Systems, where he initiated the company's product security program by defining and implementing Cisco's secure development lifecycle. He also made significant contributions to security products and network security management solutions for large enterprises and service providers.
John resides in San Diego with his wife and two sons and enjoys traveling, gardening, cooking, and sailing.
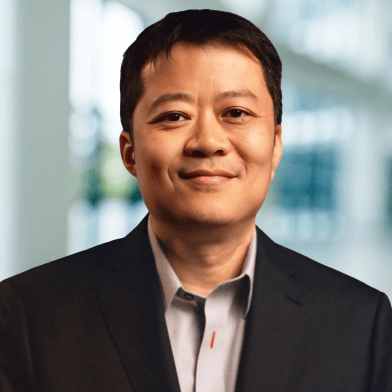
John Qian
Never Miss
an Episode
Join thousands of cloud professionals following the stories, strategies, and hard-earned lessons from the architects driving enterprise transformation. Be the first to know when new episodes go live.
Zero spam. Unsubscribe at any time.
Join cloud engineers and modern architects already tuned in.
Keep exploring
Related Episodes
How Zero Trust Was Born
Doug Merritt · Chief Executive Officer
- Trust is a human emotion, not a network concept — and treating it as one creates the vulnerabilities attackers exploit. - Focus on "protect surfaces," not everything at once. Defend your most critical assets individually, and Zero Trust becomes incremental and non-disruptive. - All bad things happen inside of an allow rule. If something bad happened, a policy somewhere permitted it. - Stop buying products and start building policy. One consistent policy construct — who, what, when, where, why, and how — can apply across your entire environment. - Security won't improve until CEOs change how cybersecurity is incentivized. CISOs need real authority, not just accountability when things go wrong.
The New Physics of Cyber
Doug Merritt · Chief Executive Officer
- AI security M&A is moving at unprecedented speed. A category that didn't exist two years ago jumped from 10 deals last year to a projected 50–60 by year-end, as companies like CrowdStrike, Palo Alto Networks, and Akamai spend hundreds of millions to fill AI roadmap gaps. - The mega deal era is accelerating. Cybersecurity M&A is on pace to exceed last year by 10%, yet most deal values remain undisclosed, making the market harder to read than it appears. - Detection without prevention is a dead end. The industry excels at seeing threats but struggles to stop them. Investors are responding, backing prevention-oriented companies with outsized funding rounds. - Security needs to go back to first principles. Three runtime control points — identity, compute/endpoint, and network — are the foundational layers where organizations can stop attacks in progress.
Cybercrime Runs Like a Fortune 500 Company
Doug Merritt · Chief Executive Officer
- Cybercrime is organized like a business. Roles are specialized and clearly compensated, from malware developers to money launderers, making these networks resilient and hard for law enforcement to dismantle. - Ransomware economics are shifting. The cost of storing and servicing stolen data has led many groups to abandon encryption entirely in favor of extortion alone. - Lateral movement, not initial access, is the real threat. Incidents like Colonial Pipeline and Stryker show that how fast attackers spread internally matters more than how they got in. - Preparation is non-negotiable. Boards should know who's responsible for which decisions in the first 24 hours of an attack, well before one happens.
Assume Containment, Not Breach
Doug Merritt · Chief Executive Officer
- Why Nick argues the industry should shift from "assume breach" to "assume containment" — and what that changes about incident response - The guardrails-not-gates philosophy that lets developers move fast without becoming security experts - How Nick's team found a workable path through an "impossible" secure-SDLC mandate on SpaceX's Falcon codebase - Applying Elon Musk's first-principles reasoning to break security problems down to their core "whys" - Why Nick sees cloud security footholds as a societal and economic risk, not just a technical one
Chris Hughes: Not Prevention, But Resiliency
Doug Merritt · Chief Executive Officer
- CVEs are exploding — over 40,000 in 2025, with 2026 projections near 60,000 (some estimates up to 100,000) — while AI makes vulnerabilities easier to find and exploit. - Patching capacity has long lagged below 10% of the backlog; broken production risk and competing business priorities keep it there. - Security should shift from trying to prevent every incident to containing and recovering from the ones that happen. - "Human in the loop" doesn't scale against AI-driven attack volume — defenders need to fight AI with AI. - Security teams that act as collaborators, not blockers, avoid the shadow-IT workarounds that punitive policies create.