The breach isn’t the problem. The spread is. →The breach isn’t the problem. The spread is. →Measure in 5 min. Free AssessmentFree Assessment

Start Now – Secure Your Cloud Future

- Request Your Demo
Get a 30-min Demo of our Cloud Network Security Solution
Schedule a demo of our solution with a cloud specialist.
Please fill out the form below to request a demo:
Your inbox is safe. We respect your privacy. By submitting this form, you agree to our privacy policy.
Limit Blast Radius Before Any Alert Fires
Zero-days found simultaneously by AI, detection-first cannot keep pace
Avg eCrime breakout time, detection-first response is structurally too slow
Credentials exfiltrated - Fortune 500 blocked live LiteLLM C2 traffic with existing DCF policy
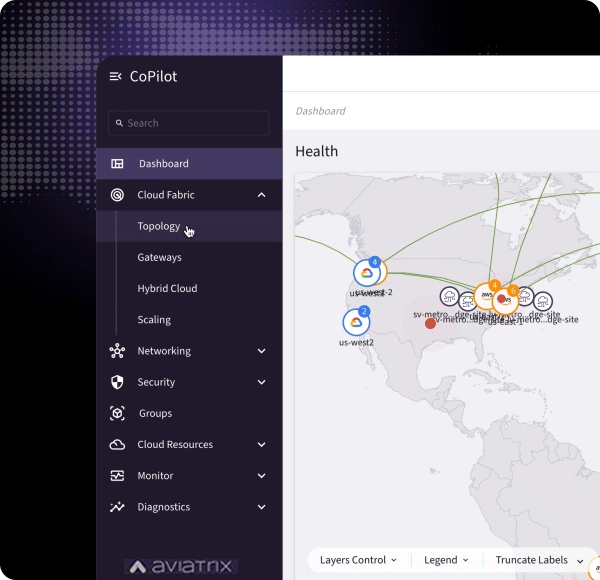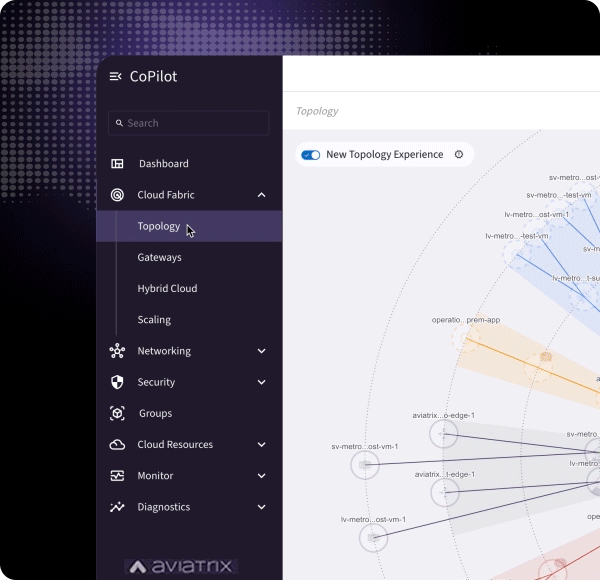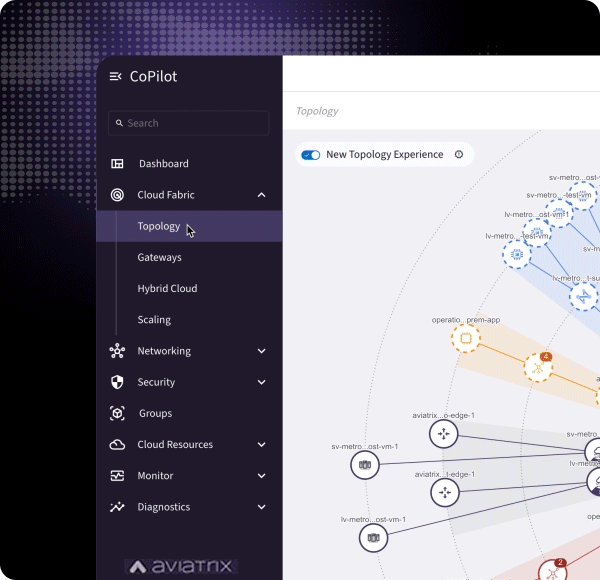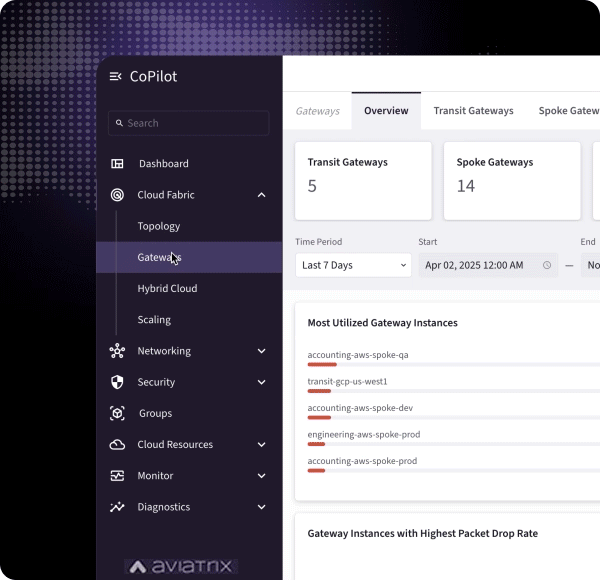
Experience the solution
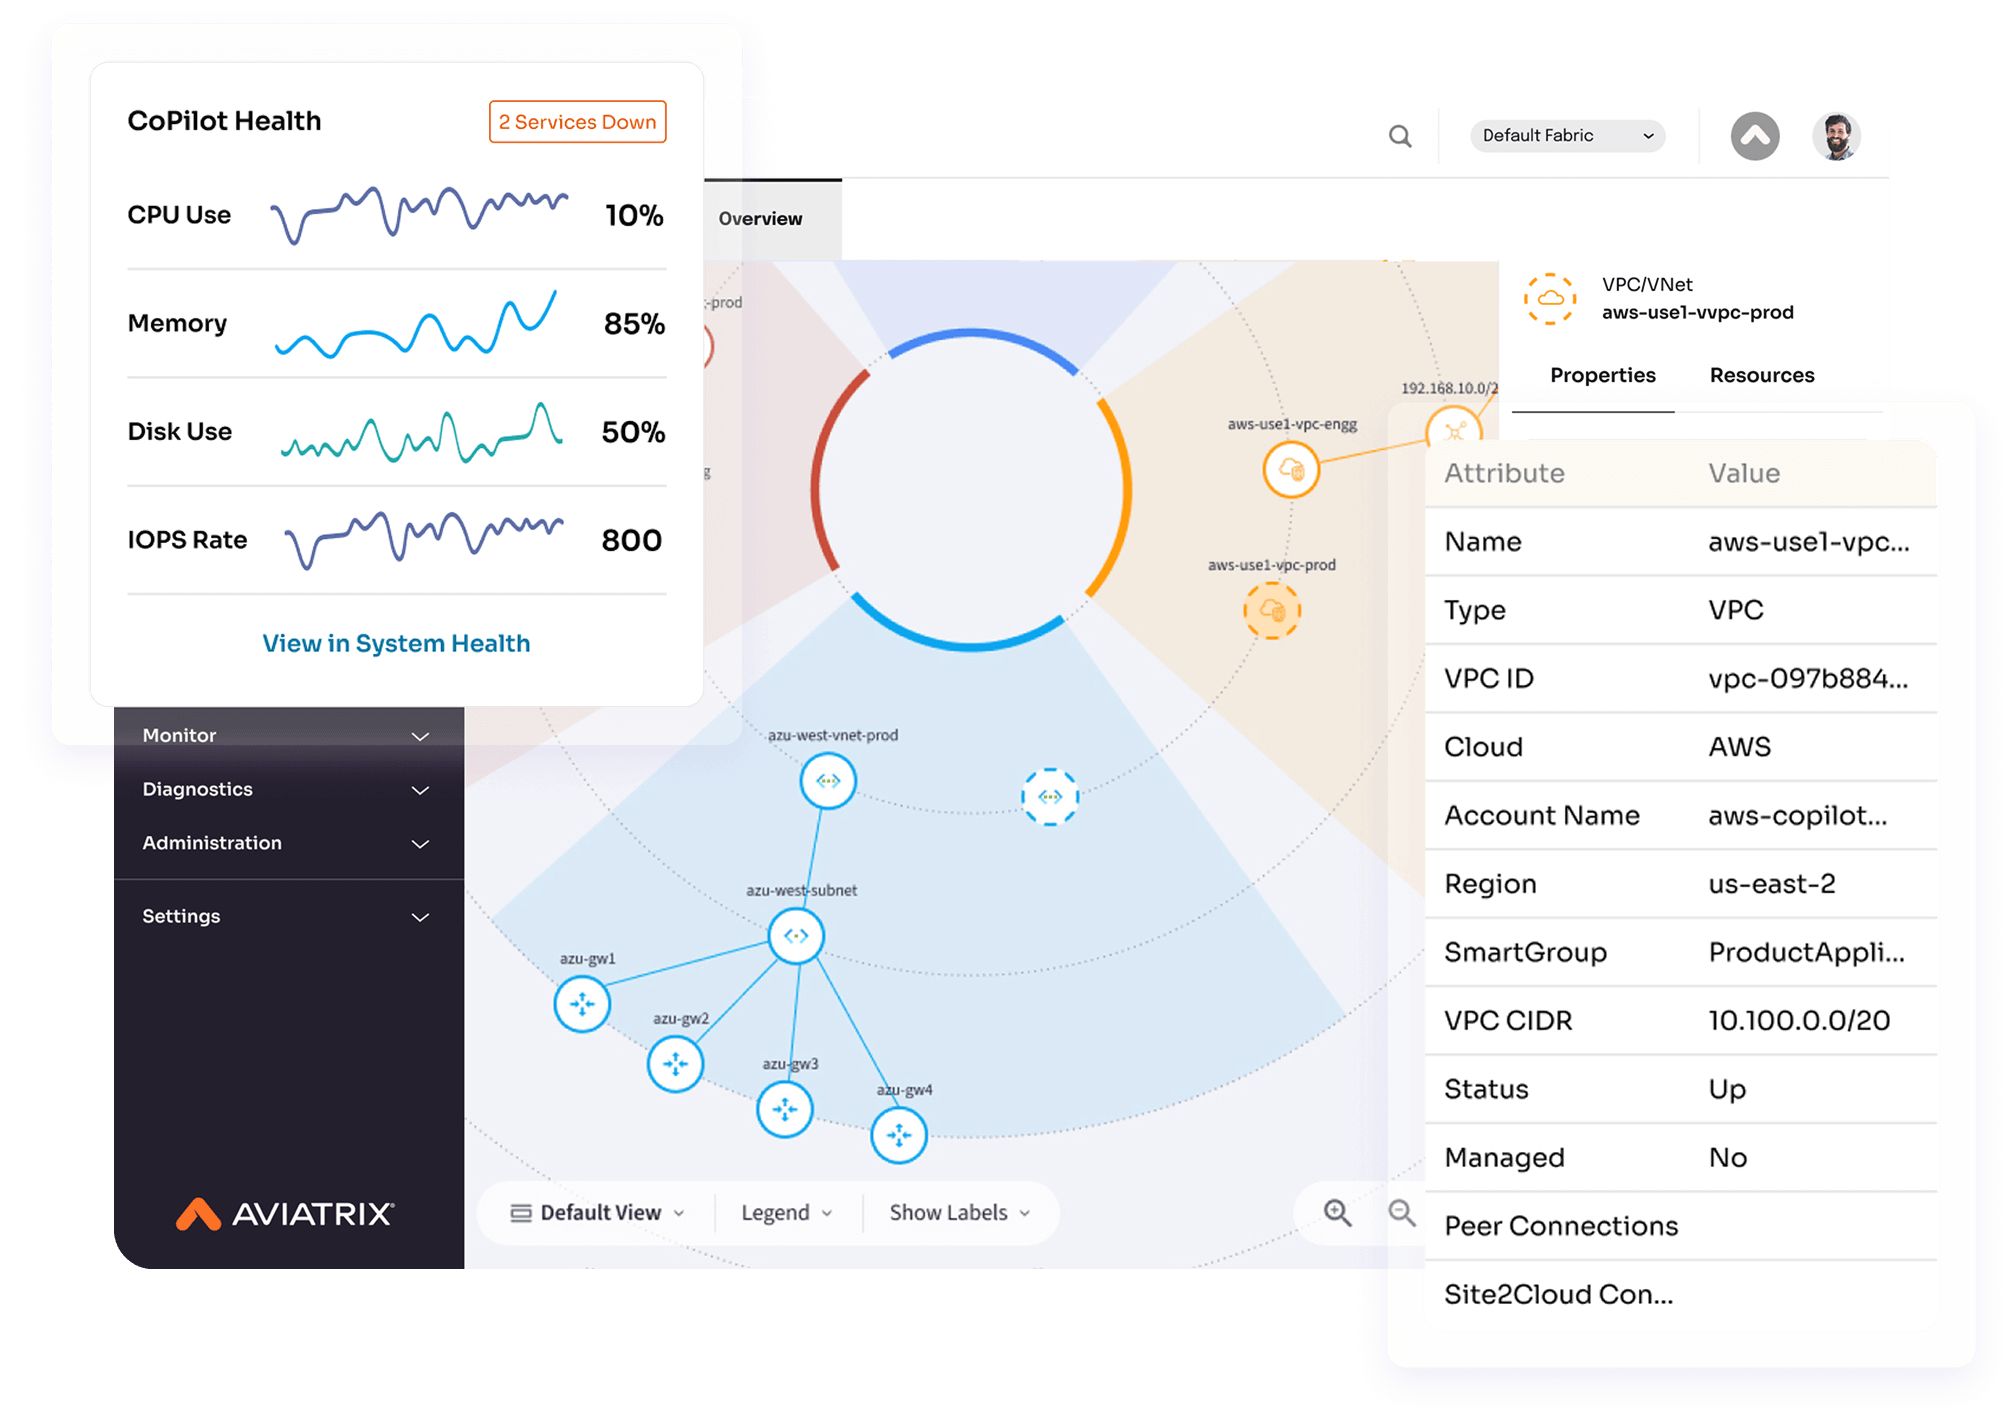
See the Containment Platform in action
Walk through a live simulation of Aviatrix — enforcement at the workload, Zero Trust segmentation, and AI egress controls. See exactly how containment limits blast radius before a breach spreads, not after.
Including 10% of the Fortune 500
500+ Enterprises Trust Aviatrix