
Executive Summary
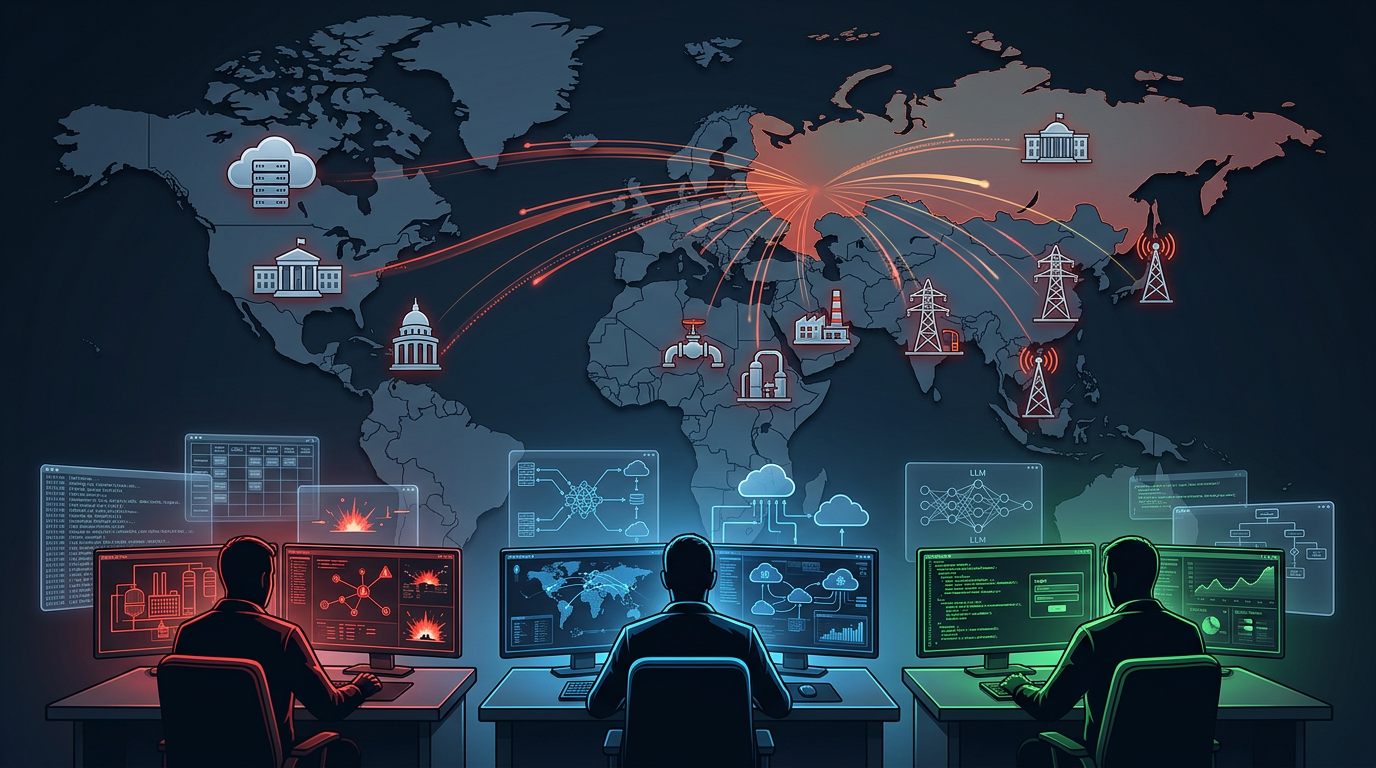
Between 2021 and 2026, Russia's cyber apparatus executed the most operationally diverse state-sponsored campaign of the period — spanning espionage, critical infrastructure sabotage, cloud identity exploitation, and destructive operations simultaneously across multiple theaters.
The defining shift: Russia's cyber operations shifted from SolarWinds‑style supply‑chain compromises to a permanent multi‑front offensive against US government, cloud providers, defense contractors, critical infrastructure, and major tech firms, repurposing Ukraine‑era wipers, ICS sabotage, and satellite disruption for global pre‑positioning, with Sandworm active across at least a dozen Western countries by 2025.
However, effective defense in 2026 requires understanding how Russian cyber tradecraft evolved from 2021 onward, not just reacting to current headlines.
The most important defensive insight:
Russia operates three distinct cyber doctrines simultaneously: GRU (Russia’s military intelligence service) units conduct destruction and critical infrastructure pre-positioning, SVR (Russia’s external/civilian intelligence agency) conducts patient strategic espionage through cloud and identity exploitation, and FSB (Russia’s main internal security and counterintelligence service) conducts targeted credential theft and influence operations. Each requires a fundamentally different detection approach. The techniques battle-tested during regional conflicts have been operationalized for use against US and Western enterprise targets.
This article analyzes that progression and translates it into concrete detection and defensive strategy guidance.
Detection & Strategy DisclaimerThe thresholds and detection logic in this document are illustrative, not prescriptive. Values such as replay windows, exfil size limits, burst timing, or file modification rates must be tuned to your environment. Network design, workforce geography, cloud setup, logging depth, and normal user behavior all affect what is "anomalous." There is no universal threshold — only environment-calibrated detection.
Strategic Context: Why It Matters to Defenders
Russia's cyber operations are not opportunistic — they are doctrinally integrated with intelligence objectives, executed by organizationally distinct units with different mandates, risk tolerances, and tradecraft profiles.
Understanding which Russian organization is operating against you fundamentally changes your detection strategy: GRU operations are faster, louder, and destructive; SVR operations are patient, cloud-native, and designed for long-duration collection; FSB operations are targeted, credential-focused, and paired with influence objectives.
Strategic Shift
Russian cyber operations transitioned from the SolarWinds-era supply chain model (patient, singular, high-value) to a permanent multi-front operational tempo — conducting strategic espionage against US cloud infrastructure, pre-positioning in Western critical infrastructure, targeting US defense and technology sectors, and conducting credential theft campaigns against policy influencers and research institutions.
The trajectory is clear: Russia's cyber units are now permanently operating at elevated tempo against US and Western targets, with tradecraft refined through years of high-intensity operations now applied globally.
Part I — Strategic Pattern (2021 → 2026)
Russian cyber operations from 2021–2026 show four consistent characteristics:
Organizational specialization — GRU (destruction/pre-positioning), SVR (strategic espionage), FSB (targeted collection/influence) operate with distinct mandates and tradecraft
Global pre-positioning — destructive capabilities developed and refined during regional conflicts are now being pre-positioned across US and Western critical infrastructure
Cloud identity pivot — SVR shifted from on-premises supply chain attacks to cloud-native identity exploitation (OAuth abuse, token theft, password spray)
Destructive capability industrialization — GRU demonstrated the ability to produce 9+ distinct wiper families in 12 months, an industrial-scale destructive malware development pipeline now available for future use against any target
The tactical stack evolved dramatically, but the doctrine remained consistent:
Gain access through identity exploitation, edge device compromise, or supply chain
Persist through cloud infrastructure embedding, legitimate tooling, or firmware-level access
Collect intelligence at scale (SVR) or pre-position for disruption (GRU)
Execute destruction when geopolitically or militarily useful
What Changed in Russian Cyber Operations (2021–2026)
Destructive Operations Became Industrialized
Between January and December 2022, GRU units deployed at minimum 9 distinct wiper malware families: WhisperGate, HermeticWiper, IsaacWiper, CaddyWiper, DoubleZero, AcidRain, Industroyer2, SwiftSlicer, and ZEROLOT. This was not a single weapon fired once — it was an industrial malware production line. AcidRain alone disrupted satellite internet across Europe, demonstrating that these capabilities are not regionally contained. By 2025, Sandworm attacked Poland's energy grid — the largest cyber attack on Polish infrastructure in years.
Defensive takeaway: Russia has demonstrated the capability to produce and deploy novel destructive malware at a pace that exceeds signature-based detection cycles. This industrial capacity can be redirected to US targets. Behavioral detection of pre-destruction staging (VSS deletion, backup destruction, mass file access) is the only reliable defense against novel wipers.
Cloud Identity Became the Primary Espionage Vector
Midnight Blizzard (APT29/SVR) compromised Microsoft's own corporate environment in January 2024 using a password spray attack against a legacy test tenant lacking MFA. The SVR didn't break encryption or exploit a zero-day — they guessed the password to a forgotten test account. From that foothold, they pivoted via a legacy OAuth application to access senior leadership email, source code repositories, and internal systems.
Defensive takeaway: Legacy OAuth applications, dormant service accounts, and test tenants without MFA are the SVR's preferred initial access vector. Your cloud identity hygiene is your Russia defense posture. Audit all OAuth app registrations, enforce MFA on every account including service principals, and eliminate legacy test environments.
Critical Infrastructure Pre-Positioning Became Global
Russia's ICS and OT capabilities — demonstrated through Industroyer2 (power grid targeting), AcidRain (satellite communications disruption across Europe), and coordinated wiper deployments against energy facilities — represent a proven playbook that has since expanded beyond its original theater. Sandworm's BadPilot campaign (disclosed February 2025) confirmed active targeting of energy, telecommunications, and government organizations in the US, UK, Canada, and Australia.
Defensive takeaway: Organizations in energy, telecommunications, and critical infrastructure should treat US-Russia geopolitical tensions as a direct trigger for elevated monitoring of OT/ICS systems, satellite communications infrastructure, and network edge devices. The capabilities are proven; the targeting is now global.
Infrastructure Parasitism as Operational Model
Turla (Secret Blizzard/FSB) didn't just build its own C2 infrastructure — it hijacked C2 belonging to other threat actors. In 2024, Microsoft documented Turla compromising Storm-0156 (a Pakistan-based espionage group), deploying its own implants (TinyTurla, TwoDash) through the compromised group's existing access and confiscating their tools (CrimsonRAT, Wainscot) for its own use.
Defensive takeaway: Finding a known APT's implant does not mean you have fully scoped the intrusion. If Turla is riding on another group's access, your IOC-based detection will identify the wrong actor, and your remediation will miss the deeper compromise.
Credential Phishing Became AI-Enhanced and Platform-Diverse
Star Blizzard (FSB/COLDRIVER) conducted sustained credential phishing campaigns against academia, defense, NGOs, and think tanks — evolving from email-based spear-phishing to WhatsApp-based social engineering by late 2024. The campaigns use extensive pre-attack research, establish rapport over weeks before delivering credential harvesting links, and deploy EvilGinx2 to defeat MFA.
Defensive takeaway: Star Blizzard's social engineering is slow, personalized, and increasingly platform-diverse (email → Teams → WhatsApp). Detection must extend beyond email gateway to cover collaboration platforms. Phishing-resistant MFA (FIDO2) is the definitive control.
AI-Enabled Malware and Rapid Exploit Weaponization Arrived
In 2026, LAMEHUG — the first confirmed Russian APT malware leveraging a large language model (Qwen2.5-Coder via Hugging Face API) for dynamic command generation. Separately, APT28's Operation Neusploit weaponized CVE-2026-21509 (Microsoft Office/MSHTML) within 24 hours of public disclosure. CrowdStrike's 2026 Global Threat Report documented an 89% increase in AI-enabled attacks and noted 82% of intrusions in 2025 were malware-free.
Defensive takeaway: The combination of AI-assisted malware and near-zero-day weaponization timelines compresses the defender's response window dramatically. Patch SLAs for internet-facing Microsoft products must be measured in hours, not days. Behavioral detection for anomalous LLM API calls (Hugging Face, OpenAI, etc.) from endpoint processes should be investigated as potential AI-enabled C2.
Current Target Prioritization
Detection Posture Adjustment
The following priorities should be elevated for any organization in Tier 1 or Tier 2:
Cloud identity hygiene audit — Enumerate all OAuth application registrations, service principals, and legacy test tenants. Any account without MFA is an SVR target. Midnight Blizzard's Microsoft breach began with a password spray against a single unprotected test account.
Edge device vulnerability management — Sandworm's BadPilot campaign exploits known vulnerabilities in Exchange, Fortinet, ConnectWise, and Outlook. Any unpatched internet-facing application is an active target for initial access.
OT/ICS network segmentation verification — If you operate energy, water, or telecommunications infrastructure, verify OT/IT segmentation and monitor for any IT-to-OT lateral movement. Sandworm has confirmed targeting of US energy and telecom sectors; Industroyer2 demonstrated ICS-specific attack capability.
Destructive malware pre-staging detection — Monitor for VSS deletion (vssadmin delete shadows), backup destruction (wbadmin delete), and mass file access patterns. Russia's wiper deployments are preceded by hours-to-days of pre-staging activity.
Residential proxy awareness — SVR operations route through residential proxy infrastructure to blend with legitimate traffic. Long-duration HTTPS connections to residential ISP IP ranges warrant investigation.
Collaboration platform credential theft — Star Blizzard now operates across email, Teams, and WhatsApp. Extend phishing detection beyond email to all collaboration platforms used by high-value targets.
Threat Actor Landscape
Key distinction: Russia operates cyber units across three intelligence agencies with fundamentally different mandates:
GRU units (APT28, Sandworm, Cadet Blizzard): Military intelligence — willing to conduct destructive operations, ICS sabotage, and high-tempo offensive campaigns against Western targets. Multiple distinct units (26165, 74455, 29155) with different specializations, now operating at sustained elevated tempo.
SVR (APT29/Midnight Blizzard): Foreign intelligence collection — patient, technically sophisticated, focused on cloud infrastructure and identity exploitation for long-duration access to government and technology targets.
FSB units (Turla, Gamaredon, Star Blizzard): Security service operations — ranging from sophisticated persistent espionage (Turla) to high-volume targeted collection (Gamaredon) to credential theft and influence targeting US/Western policy circles (Star Blizzard).
Attribution note: GRU Unit 29155 (Cadet Blizzard) was only formally attributed in 2023, despite being active since at least 2020. This unit operates with less technical sophistication than Sandworm or APT28 but compensates with high operational aggression — it deployed WhisperGate with no attempt at stealth. The US Department of State has offered a $10 million reward for information on Unit 29155 operatives.
Part II — Campaign Evolution Analysis (2021–2026)
2021: SolarWinds Aftermath and Federated Auth Targeting
Characteristic: SVR continued exploitation of SolarWinds-era access against US government and technology targets; development of AD FS persistence techniques
Tooling: NOBELIUM custom tooling, FoggyWeb (AD FS backdoor), MagicWeb (authentication bypass)
Detection profile: LOW for SVR (cloud-native, legitimate API abuse); MEDIUM for GRU (traditional tooling)
Defining campaign: APT29 FoggyWeb — backdoor targeting AD FS servers to extract token-signing certificates and deploy additional payloads; enabled persistent access to US federated authentication infrastructure
2022: Industrial-Scale Destructive Capability Demonstrated
Characteristic: Unprecedented deployment of destructive malware; 9+ wiper families in 12 months; ICS targeting; satellite communications disruption extending across Europe
Tooling: WhisperGate, HermeticWiper, IsaacWiper, CaddyWiper, AcidRain, Industroyer2, SwiftSlicer, DoubleZero, ZEROLOT
Detection profile: VARIED — wipers are detectable in pre-staging phase but novel at deployment; ICS malware requires specialized OT monitoring
Defining campaigns: AcidRain (Viasat satellite modem wiper affecting internet service across Europe — not regionally contained); Industroyer2 (ICS-specific malware targeting power grid IEC-104 protocol); HermeticWiper and WhisperGate (destructive operations attributed to distinct GRU units 74455 and 29155 respectively)
2023: Cloud Identity Exploitation and Zero-Day Campaigns
Characteristic: SVR pivoted to cloud-native attacks targeting US organizations; APT28 exploited Outlook zero-day for 20+ months across 14 NATO nations; attribution clarity improved
Tooling: OAuth application abuse, password spray infrastructure, CVE-2023-23397 (Outlook NTLM relay), CVE-2023-42793 (JetBrains TeamCity)
Detection profile: LOW for SVR cloud operations (legitimate API usage); MEDIUM for APT28 (NTLM relay detectable)
Defining campaigns: Midnight Blizzard Teams social engineering against US targets (August 2023); APT28 Outlook NTLM relay exploitation against 30+ organizations in 14 nations (April 2022–October 2023, disclosed March 2023); Cadet Blizzard formally attributed to GRU Unit 29155
2024: US Corporate Breach Escalation and Global Expansion
Characteristic: SVR breached Microsoft and TeamViewer corporate environments — demonstrating direct targeting of US technology providers; Sandworm expanded to 15+ countries; Turla hijacked rival APT infrastructure
Tooling: Password spray + OAuth pivot (Midnight Blizzard); CVE-2024-1709 (ConnectWise), CVE-2023-48788 (Fortinet); TinyTurla, TwoDash (Turla via hijacked C2)
Detection profile: LOW for SVR (legitimate credential use from residential proxies); MEDIUM for Sandworm BadPilot (known CVE exploitation)
Defining campaigns: Midnight Blizzard Microsoft breach (January 2024 — accessing senior leadership email, source code, and internal systems; 10x escalation in February); TeamViewer corporate breach (June 2024); Midnight Blizzard large-scale RDP file spear-phishing (October 2024); Turla hijacking Storm-0156 C2 infrastructure; Star Blizzard WhatsApp pivot (November 2024)
2025–2026: Persistent Access at Scale, AI-Enabled Operations, and Rapid Exploit Weaponization
Characteristic: Sandworm BadPilot campaign confirmed targeting US, UK, Canada, and Australia; SVR watering-hole campaigns exploiting device code authentication against US organizations; APT28 weaponizing CVEs within 24 hours of disclosure; Star Blizzard adopted iOS exploit kits; LLM-enabled malware appeared; pro-Russia hacktivist groups coordinated OT attacks on US critical infrastructure
Tooling: ZeroLot wiper, device code authentication abuse, EvilGinx2, residential proxy networks, LAMEHUG (LLM-enabled malware using Hugging Face API), DarkSword iOS exploit kit, BadPaw/MeowMeow malware families, CVE-2026-21509 (MSHTML zero-day)
Detection profile: LOW for SVR (cloud-native, device code auth abuse); MEDIUM for Sandworm (known CVE exploitation at scale); HIGH velocity for APT28 (zero-day weaponized within 24 hours)
Defining campaigns:
APT28 Operation Neusploit (February 2026): Exploited CVE-2026-21509 (Microsoft Office/MSHTML zero-day) within 24 hours of public disclosure, targeting Central/Eastern European government and defense entities — demonstrating near-zero delay between vulnerability disclosure and weaponization
APT28 LAMEHUG malware (CrowdStrike 2026 GTR): Deployed LLM-enabled malware leveraging Qwen2.5-Coder-32B-Instruct via Hugging Face API for dynamic command generation — first confirmed Russian APT use of generative AI in operational malware
Star Blizzard DarkSword iOS exploit kit (March 2026): Adopted commercial iOS exploit kit targeting government, academia, financial, and legal entities — marking a shift from credential theft to full endpoint compromise including mobile devices
Sandworm Poland energy grid attack (January 2026): Data-wiping malware deployed against Polish energy systems — the largest cyber attack on Polish infrastructure in years, confirming continued willingness to target NATO member critical infrastructure
APT29 device code authentication abuse (2025–2026): Watering-hole campaigns tricking US government and enterprise users into authorizing attacker-controlled devices via Microsoft device code authentication flow
Pro-Russia hacktivist OT attacks (CISA advisory December 2025): CARR, Z-Pentest, NoName057(16), and Sector16 conducting coordinated attacks on US water/wastewater, food & agriculture, and energy OT systems via exposed VNC connections
Mandiant M-Trends 2026: 500,000+ hours of incident investigations in 2025 confirm resurgence of Russian cyber operations and information operations supporting Russian strategic interests
Part III — Full Kill Chain: Phase-by-Phase TTPs with Detection Logic
Phase 1 – Reconnaissance
Phase 2 – Initial Access
Key CVEs Exploited (2021–2026):
CVE-2021-34473 / CVE-2021-34523 / CVE-2021-31207 (ProxyShell — Exchange)
CVE-2022-41352 (Zimbra)
CVE-2022-26318 (WatchGuard Firebox)
CVE-2023-23397 (Outlook NTLM relay — APT28)
CVE-2023-42793 (JetBrains TeamCity — APT29)
CVE-2023-38831 (WinRAR — APT28)
CVE-2023-48788 (Fortinet FortiClient EMS — Sandworm)
CVE-2024-1709 (ConnectWise ScreenConnect — Sandworm)
CVE-2022-38028 (Windows Print Spooler — APT28, GooseEgg tool)
CVE-2026-21509 (Microsoft Office/MSHTML — APT28, Operation Neusploit, weaponized within 24h of disclosure)
Phase 3 – Execution & Persistence
Phase 4 – Privilege Escalation & Defense Evasion
Phase 5 – Credential Access
Phase 6 – Lateral Movement
Phase 7 – Collection & Exfiltration
Phase 8 – OT/ICS Targeting
Why Industroyer2/AcidRain are uniquely dangerous:
Industroyer2 targets IEC-104 protocol directly — purpose-built for electric grid disruption
AcidRain is a generic wiper that targets embedded Linux devices — easily redeployable against any modem, router, or IoT device
Both demonstrate Russia's capability to attack infrastructure layers below endpoint visibility
Phase 9 – Impact (Destructive Operations)
Detection Engineering Master Matrix
Part IV — Threat Hunt Hypotheses
Disclaimer:These hunts complement EDR/ITDR and other security tool alerting. Mature platforms may detect portions or most of this activity, but correlation, tuning, and escalation logic determine whether intrusion is caught pre-impact or post-destruction.
Hunt 1: Midnight Blizzard — Orphaned OAuth Applications
Hypothesis: Legacy OAuth applications with elevated permissions are being abused for mailbox access without interactive sign-in.
Note: Mature ITDR platforms may alert on anomalous OAuth activity — validate coverage before building custom logic.
Core Detection Logic:
Enumerate all OAuth app registrations in Entra ID with Mail.Read, Mail.ReadWrite, Mail.Send, or full_access_as_app permissions
Cross-reference against approved application inventory
Flag: Any app not in approved inventory with mail permissions = immediate review
Secondary: OAuth app accessing >10 distinct mailboxes OR mailboxes of executives/security team
High Confidence: Any legacy OAuth app (created >1 year ago) with mail permissions that was not recently re-consented by an admin = HIGH risk. Midnight Blizzard specifically targets dormant, forgotten applications.
Hunt 2: APT28 — Outlook NTLM Relay Artifacts
Hypothesis: Crafted calendar/task items with UNC paths triggering automatic NTLM authentication to attacker-controlled servers.
Core Detection Logic:
Search Exchange mailbox items (calendar entries, tasks, notes) for properties containing UNC paths (\\IP\share or \\hostname\share)
Correlate with outbound SMB (TCP 445) or WebDAV traffic to external IPs
Check for Impacket ntlmrelayx signatures on network perimeter
Alert Threshold: Any Exchange item containing UNC path to external IP = CRITICAL. No legitimate business reason for calendar items to reference external file shares via UNC.
Hunt 3: Sandworm — Pre-Wiper Staging Activity
Hypothesis: GRU operator is preparing environment for destructive wiper deployment.
Core Detection Stack (correlate within 48h window, tune per environment):
vssadmin delete shadows /allwbadmin delete catalog -quietorwbadmin delete systemstatebackupbcdedit /set {default} recoveryenabled NoGPO modification with script deployment to server OUs
SYSVOL write of executable/script files
Escalation Logic:
1 indicator → HIGH
2+ indicators on same host or within same AD site → CRITICAL (assume imminent wiper deployment)
GPO modification + SYSVOL script + VSS deletion = CRITICAL — initiate containment immediately
CRITICAL: Russia's historical wiper deployments were preceded by hours (not weeks) of pre-staging. If these capabilities are turned against US targets, detection-to-containment SLA must be measured in minutes, not days.
Hunt 4: Residential Proxy Password Spray
Hypothesis: SVR is conducting low-volume password spray through distributed residential proxy infrastructure to avoid lockout thresholds.
Core Detection Logic:
Aggregate all Entra ID sign-in failures over 24h rolling window
Filter for source IPs mapping to residential ISP ASNs (not commercial/VPN/enterprise)
Correlate: >20 distinct residential IPs attempting auth against same tenant with <5 attempts per IP
Secondary: Successful auth from residential IP immediately following distributed failure pattern
Alert Threshold: Distributed residential-IP auth failures across >10 IPs targeting same tenant within 24h = HIGH. Successful login from residential IP after failure pattern = CRITICAL.
Hunt 5: AD FS / Federated Authentication Backdoor
Hypothesis: APT29 has backdoored AD FS to forge authentication tokens (FoggyWeb / MagicWeb pattern).
Core Detection Logic:
Audit all DLLs loaded by AD FS service process against known-good baseline
Check AD FS configuration database for unauthorized modifications
Monitor access to DKM (Distributed Key Management) container in Active Directory
Verify token-signing certificate has not been exported or duplicated
Alert Threshold: Any unexpected DLL in AD FS process = CRITICAL. Any DKM container access from non-AD-FS server = CRITICAL. Token-signing certificate export event = CRITICAL. These are definitive indicators of authentication infrastructure compromise.
Hunt 6: Turla — Multi-Actor Infrastructure Overlap
Hypothesis: Turla is operating through C2 infrastructure belonging to another threat actor, making attribution and scoping incomplete.
Core Detection Logic:
For any confirmed intrusion attributed to a non-Russian APT: check for secondary implants not matching the attributed actor's known tooling
Look for TinyTurla, TwoDash, Statuezy, MiniPocket indicators alongside non-Russian APT tools
Monitor for unexplained lateral movement or data access that exceeds the attributed actor's known objectives
Alert Threshold: Finding implants from two distinct threat actors in the same environment = immediate re-scoping of incident. Turla's infrastructure parasitism means single-actor attribution may miss the more dangerous operator.
Hunt 7: Sandworm BadPilot — Edge Device Compromise
Hypothesis: Sandworm subgroup has exploited known vulnerabilities in internet-facing applications for persistent access.
Core Detection Logic:
Audit all internet-facing Exchange, Fortinet, ConnectWise ScreenConnect, and WatchGuard appliances for patch status
Check for web shells in Exchange web paths (aspnet_client, OWA/auth)
Review ConnectWise ScreenConnect for unauthorized admin accounts (CVE-2024-1709 auth bypass)
Fortinet: Check for unauthorized admin accounts or configuration changes post-CVE-2023-48788
Alert Threshold: Any unpatched internet-facing application in the BadPilot target set = assume compromised until verified. Any web shell or unauthorized admin account = CRITICAL.
Part V — Leadership Briefing: Strategic Threat Posture
The Strategic Reality
Russia's cyber threat is fundamentally different from China (patient, infrastructure-focused espionage), Iran (reactive, escalation-driven), and DPRK (financially motivated theft). Russia operates as a multi-doctrine adversary: its GRU units conduct destruction and critical infrastructure pre-positioning against Western targets, its SVR conducts patient strategic espionage through US cloud infrastructure, and its FSB conducts targeted credential theft and influence operations — all simultaneously, against overlapping target sets, with different risk tolerances and detection profiles.
The key insight: you are not facing one Russian cyber threat — you are facing three organizationally distinct threats that happen to share a flag. Each requires a different detection investment. The SVR has already breached Microsoft. Sandworm is already targeting US energy and telecom. Star Blizzard is already phishing US think tanks and defense researchers.
Three Things Leadership Must Understand
Cloud identity is the SVR's primary attack surface — and they have already compromised the providers.
Midnight Blizzard breached Microsoft's own corporate environment through a password spray against a test account without MFA. They then pivoted via a legacy OAuth application to access senior leadership email and source code. If the SVR can compromise Microsoft, your cloud tenant's security posture matters enormously. The most impactful defensive investment against SVR espionage is cloud identity hygiene: eliminate legacy OAuth apps, enforce MFA on all accounts (including test/dev/service), implement conditional access policies, and monitor the M365 Unified Audit Log continuously.
Investment priority: Complete OAuth application audit, legacy tenant cleanup, MFA enforcement on all accounts including service principals, and E5-level UAL monitoring.
Russia has demonstrated industrial-scale destructive capability — and it is now targeting the US.
GRU units proved they can produce 9+ distinct wiper families in a single year. AcidRain disrupted internet across Europe via Viasat satellite modems. By 2025, Sandworm's BadPilot campaign confirmed active targeting of US, UK, Canadian, and Australian organizations in energy, telecom, and government sectors. The destructive capability has been proven, the targeting has gone global, and the pre-positioning is underway.
Investment priority: Destructive malware pre-staging detection (VSS deletion, backup destruction, GPO-deployed scripts), OT/ICS network segmentation, and incident response playbooks that account for wiper scenarios (where "restore from backup" IS the recovery, not "patch and reimage").
The APT28 Outlook vulnerability was exploited for 20 months before disclosure — zero-click, zero-interaction.
CVE-2023-23397 required no user interaction — receiving the crafted email was sufficient to trigger NTLM authentication to the attacker's server. APT28 exploited it against 30+ organizations across 14 NATO nations for 20 months before it was patched. This is not a theoretical risk — it is a demonstrated capability where receiving an email compromises your credentials.
Investment priority: Aggressive patch management for email infrastructure (Exchange on-premises and Exchange Online), NTLM relay protections (EPA for Exchange, SMB signing, restrict outbound SMB), and credential hygiene that limits the blast radius of a stolen NTLM hash.
Risk Prioritization by Actor
This document reflects threat intelligence through March 2026, including the 2026 Annual threat reports published by reputed vendors, and campaign reporting through Q1 2026. Russia's operational tempo against US and Western targets has increased steadily since 2022 and shows no signs of abatement. When reviewing this document's currency, always check current US-Russia geopolitical status.
Master References Index
Annual Threat Intelligence Reports
Additional Vendor Reports
Government & Regulatory Advisories
Campaign-Specific Vendor Reporting (2021–2026)
MITRE ATT&CK Group Profiles
Ready to see Aviatrix in action?
Get a personalized live demo walkthrough or explore our latest deep-dive cloud threat research intelligence.

