
Executive Summary
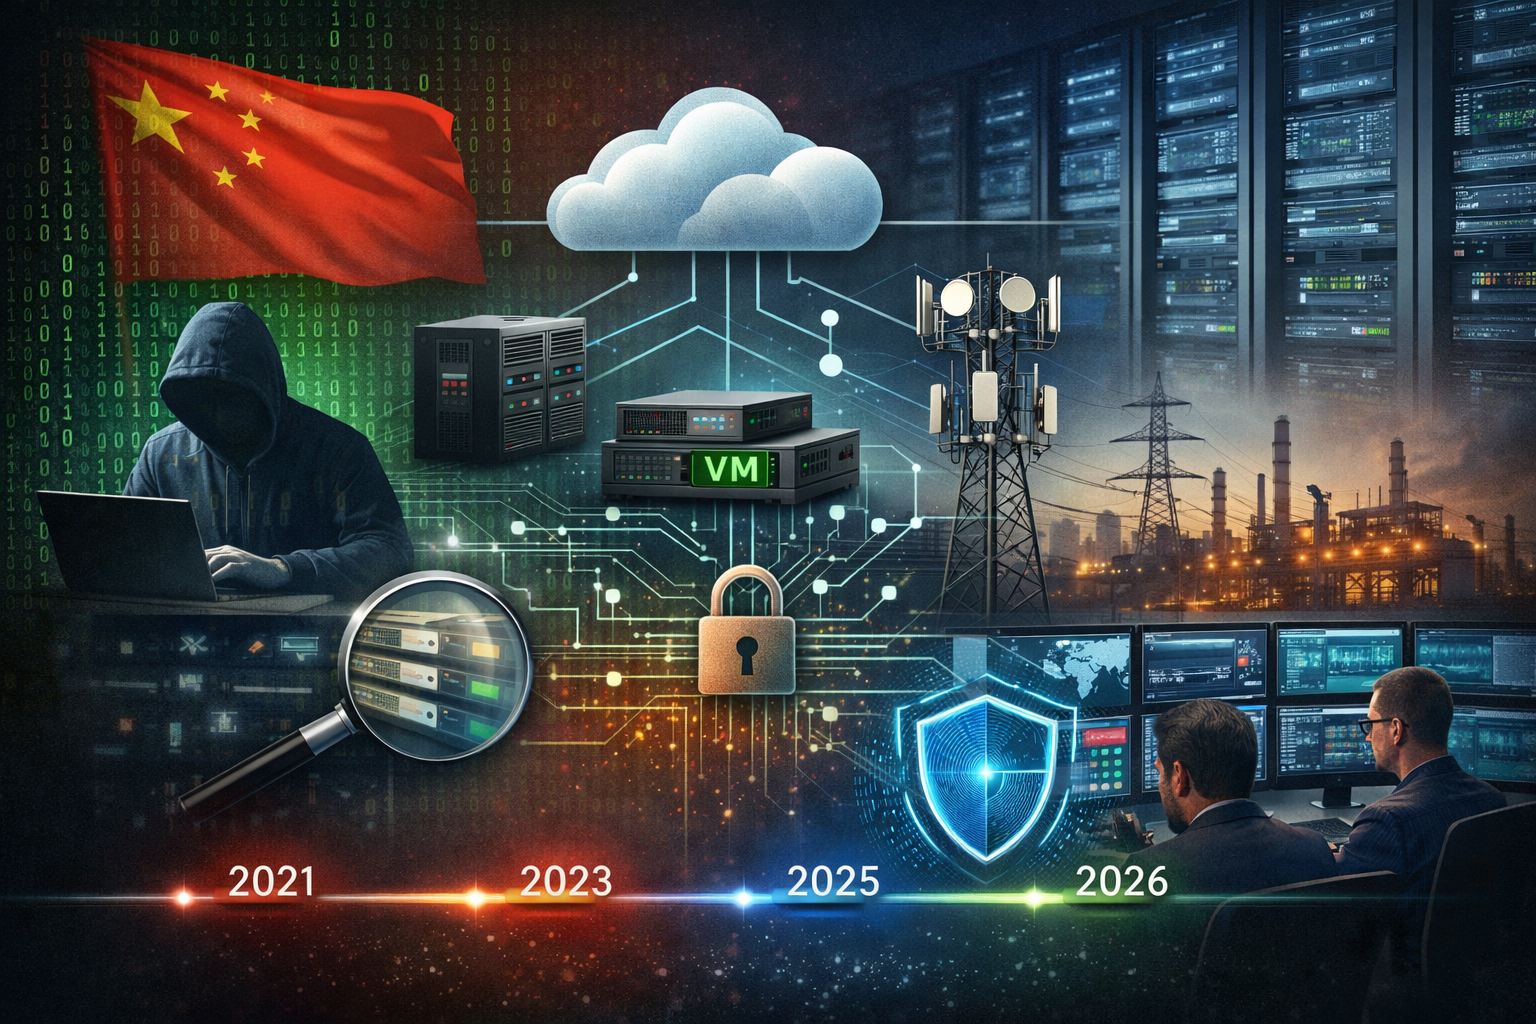
Between 2021 and 2026, PRC-affiliated threat actors executed the most consequential cyber espionage campaign in recorded history — not through sophistication alone, but through operational patience, institutional coordination, and systematic exploitation of trusted infrastructure.
The defining shift: China moved away from noisy, tool-heavy intrusions (2016–2020 vintage) toward a model where the attack surface is the infrastructure itself — edge devices, cloud identity systems, hypervisors, and telecommunications backbone. By 2025, PRC actors weren't breaking into networks from outside; they were living inside the fabric of enterprise connectivity.
However, effective defense in 2026 requires understanding how PRC cyber tradecraft evolved from 2021 onward, not just reacting to current headlines.
The most important defensive insight:
The techniques used in 2026 were built incrementally through campaigns executed between 2021 and 2025.
This article analyzes that progression and translates it into concrete detection and defensive strategy guidance.
Detection & Strategy DisclaimerThe thresholds and detection logic in this document are illustrative, not prescriptive. Values such as replay windows, exfil size limits, burst timing, or file modification rates must be tuned to your environment. Network design, workforce geography, cloud setup, logging depth, and normal user behavior all affect what is "anomalous." There is no universal threshold — only environment-calibrated detection.
Strategic Context: Why It Matters to Defenders
China's cyber operations are not opportunistic — they are doctrine-driven and institutionally coordinated.
PRC cyber strategy follows a long-horizon intelligence model: pre-position access during peacetime, collect strategically, and maintain the option for disruption during crisis.
Understanding the doctrinal arc helps you anticipate what attack surfaces will be targeted next and where to invest detection before exploitation occurs.
Strategic Shift
PRC cyber operations transitioned from bulk exploitation (ProxyLogon-era mass collection) to infrastructure-as-implant — embedding capabilities inside edge devices, cloud identity systems, hypervisors, and telecom backbone equipment that defenders cannot inspect with traditional endpoint tools.
The trajectory is clear: the implant is becoming the infrastructure itself.
Operational Implication for SOC & Threat Hunters
Geopolitical flashpoints between Washington and Beijing are no longer abstract policy issues—they are direct, early-warning triggers for People's Republic of China (PRC) state-sponsored cyber operations.
Part I — Strategic Pattern (2021 → 2026)
PRC cyber operations from 2021–2026 show four consistent characteristics:
Operational patience — dwell times measured in years, not days
Infrastructure-level targeting — edge devices, cloud identity, hypervisors, telecom backbone
Minimal tooling footprint — living-off-the-land on network devices; no custom malware to detect
Institutional coordination — multiple units (MSS, PLA, contracted groups) with distinct mandates but shared access infrastructure
The tactical stack evolved dramatically, but the doctrine remained consistent:
Gain access below visibility of endpoint tools
Persist through patching and remediation
Collect intelligence at scale
Maintain disruption option for future crisis
What Changed in PRC Cyber Operations (2021–2026)
1. Mass Exploitation Gave Way to Surgical Infrastructure Compromise
ProxyLogon (2021) saw HAFNIUM exploit 400,000+ Exchange servers indiscriminately. By 2024–2025, Salt Typhoon was surgically embedded inside US telecom carriers for 12+ months before detection — accessing CALEA wiretap systems to read US law enforcement surveillance feeds.
Defensive takeaway: Volume-based detection that worked against ProxyLogon-era attacks will miss Salt Typhoon-style operations entirely. Detection must shift to behavioral anomalies on infrastructure devices.
2. Cloud Identity Became the Primary Attack Surface
Storm-0558 (2023) forged Azure AD tokens using a stolen Microsoft consumer signing key — accessing ~25 government organizations' email without triggering any authentication event. The compromise occurred at the provider level, not the customer level.
Defensive takeaway: Your cloud security controls are downstream of a trust relationship with the provider. Monitor for mail access without corresponding sign-in events. M365 E5 UAL logging is not optional for high-risk organizations.
3. Edge Device Implants Designed for Decade-Scale Persistence
SPAWN (2025) was not a traditional implant — it was an implant ecosystem built to survive firmware re-flash, factory reset, and legitimate security patches on Ivanti devices. SPAWNANT patches the upgrade mechanism itself to re-inject malware during legitimate updates.
Defensive takeaway: Standard IR playbooks (isolate → patch → restore) do not work against SPAWN. Hardware replacement is the only guaranteed remediation.
4. Hypervisor Targeting as Domain-Equivalent Access
BRICKSTORM (2022–2025) targeted VMware vCenter/ESXi — one compromised hypervisor provides access to every VM on that host, regardless of guest OS patching, EDR coverage, or network segmentation.
Defensive takeaway: ESXi hosts should be treated as Tier 0 assets (equivalent to domain controllers). VIB installations, SSH access, and VM clone events require active monitoring.
5. Pre-Positioning for Future Disruption
Volt Typhoon maintained access to US critical infrastructure (energy, water, transport) using exclusively living-off-the-land techniques — no custom malware, no suspicious traffic, no network anomalies. The strategic goal: maintain persistent access as a deterrence and wartime disruption capability.
Defensive takeaway: Volt Typhoon-style pre-positioning has near-zero detection profile with conventional tools. Network segmentation, identity hygiene, and edge device integrity verification are the primary controls.
Current Target Prioritization
PRC targeting operates on strategic intelligence priorities:
Detection Posture Adjustment
The following priorities should be elevated for any organization in Tier 1 or Tier 2:
Edge device integrity verification — Ivanti, Fortinet, Cisco, Juniper appliances in your environment should be checked against vendor ICT tools and known-good baselines. Any unpatched device is an active target.
Hypervisor audit — Review all ESXi VIB installations, SSH access logs, VM clone events, and startup scripts. Unauthorized VIB with
CommunitySupportedacceptance = immediate investigation.M365 UAL monitoring — Mail access (
MailItemsAccessed) without corresponding sign-in events from the same IP/AppId is the definitive Storm-0558-style indicator. Requires E5 licensing.Telecom/ISP anomaly detection — For telecom sector: audit all Cisco IOS-XE management interface access, policy-based routing changes, and CALEA system access logs.
ORB network awareness — Outbound HTTPS connections to residential ISP IP ranges with long duration and no associated domain = potential Operational Relay Box (ORB) C2.
Threat Actor Landscape
Key distinction: PRC operates units across MSS (Ministry of State Security), PLA (People's Liberation Army), and contracted private groups, with different mandates:
MSS units (APT41, APT10, Storm-0558): Intelligence collection, technology theft, both state-tasked and moonlighting financially-motivated operations
PLA/strategic units (Salt Typhoon, Volt Typhoon): Infrastructure access, pre-positioning, signals intelligence — patient, low-noise, long-duration
IRGC-equivalent contractors: Groups like UNC5221 that operate semi-independently, targeting edge devices with zero-day exploitation
Attribution note: Attribution between groups is fluid. APT41/VAULT PANDA operates with state sanction but conducts financially-motivated operations on the side — making them uniquely dangerous as they maintain operational tempo even without direct state tasking.
Part II — Campaign Evolution Analysis (2021–2026)
2021: Volume and Velocity (ProxyLogon Era)
Characteristic: Mass exploitation of internet-facing services with web shell implants
Tooling: China Chopper, custom ASPX web shells, open-source tools (Mimikatz, Cobalt Strike)
Detection profile: HIGH — web shells are detectable, tool signatures are known, network traffic is noisy
Defining campaign: ProxyLogon — HAFNIUM weaponized 0-days at nation-scale within 72 hours; 400,000+ Exchange servers exposed; at least 10 threat groups adopted exploit within days
2022–2023: Identity and Stealth (Storm-0558 Era)
Characteristic: Cloud identity exploitation, token forgery, API-based mail access
Tooling: Custom token generation, legitimate Microsoft Graph/EWS APIs
Detection profile: LOW — no malware, no web shells, uses legitimate Microsoft APIs with valid tokens
Defining campaign: Storm-0558 — forged Azure AD tokens using stolen MSA consumer signing key; accessed ~25 government organizations' email; no authentication events generated
2023–2025: Infrastructure as Implant (Salt Typhoon / SPAWN Era)
Characteristic: Compromise the network infrastructure itself; implants that outlast IR response
Tooling: Custom firmware implants (SPAWN ecosystem), network traffic interception, BRICKSTORM hypervisor backdoor
Detection profile: VERY LOW — the implant IS the network device; no separate malware process to detect
Defining campaigns: Salt Typhoon (telecom backbone, CALEA access); SPAWN (Ivanti firmware persistence surviving factory reset); BRICKSTORM (VMware vCenter/ESXi backdoor, 393-day average dwell time)
2025–2026: Pre-Positioning at Scale
Characteristic: Volt Typhoon-style pre-positioning in critical infrastructure — not for current intelligence but for future sabotage capability
Tooling: Living-off-the-land on network devices (no custom malware), dormant capabilities
Detection profile: Near-zero — no novel tools, no suspicious traffic, no network anomalies
Emerging: APT41 DodgeBox/MoonWalk with environmental keying (payload only decrypts on the target machine); AI-assisted reconnaissance
Part III — Full Kill Chain: Phase-by-Phase TTPs with Detection Logic
Phase 1 – Reconnaissance
Phase 2 – Initial Access
Key CVEs Exploited (2021–2025):
CVE-2021-26855 / CVE-2021-27065 (ProxyLogon)
CVE-2023-20198 / CVE-2023-20273 (Cisco IOS-XE)
CVE-2023-46805 / CVE-2024-21887 (Ivanti Connect Secure)
CVE-2024-21762 (Fortinet SSL-VPN)
CVE-2025-0282 / CVE-2025-22457 (Ivanti Connect Secure)
Phase 3 – Execution & Persistence
Phase 4 – Privilege Escalation & Defense Evasion
Phase 5 – Credential Access
Phase 6 – Lateral Movement
Phase 7 – Collection & Exfiltration
Detection Engineering Master Matrix
Part IV — Threat Hunt Hypotheses
Disclaimer: These hunts complement EDR/ITDR alerting. Mature platforms may detect portions or most of this activity, but correlation, tuning, and escalation logic determine whether intrusion is caught pre-impact or post-encryption
Hunt 1: Surviving Web Shells — Post-Patch Persistence
Hypothesis: Exchange servers patched against ProxyLogon may still contain web shells placed before the patch date.
Core Detection Logic:
Identify all
.aspxfiles in Exchange web paths (aspnet_client,OWA\\auth,ecp) with creation timestamp before March 2, 2021Filter for files <2KB with no deployment record (China Chopper shells typically <500 bytes)
Validate: any ASPX file containing
eval(),Execute(), orInvoke()of a request parameter = confirmed web shell
Alert Threshold: Any result = HIGH. No legitimate reason for pre-patch ASPX files in web root without deployment record.
Hunt 2: Storm-0558 Style — Tokenless Mail Access
Hypothesis: Forged tokens used to access mail without triggering sign-in events.
Note: Mature ITDR platforms may alert on orphaned mail access events — validate coverage before building custom logic.
Core Detection Logic:
Pull all
MailItemsAccessedfrom UAL (rolling 30-day window)Correlate on
UserId + ClientIPAddress + AppIdFlag: mail access with NO matching sign-in event within ±30 min
Secondary: non-Microsoft first-party AppId accessing >50 messages/hour
High Confidence: Zero tolerance — any mail access without correlated sign-in is anomalous. Maintain explicit allowlist for legitimate service accounts.
Hunt 3: DodgeBox Environmental Keying
Hypothesis: DodgeBox executes a specific API sequence (volume serial → hostname → username → decrypt) that is rare in legitimate software.
Core Detection Logic:
Processes from non-standard paths with no command-line arguments
All four APIs called within 5-second window:
GetVolumeInformationW,GetComputerNameW,GetUserNameW,CryptDecrypt/BCryptDecryptHigh-entropy PE from user-writable path
Alert Threshold: Any match outside known-good baseline warrants investigation. Sandbox with target-specific values to confirm environmental keying.
Hunt 4: SPAWN / BRICKSTORM — Edge Device Anomalies
Hypothesis: Infected edge devices exhibit tunneling (SPAWNMOLE) and anomalous SSH patterns (SPAWNSNAIL).
SPAWNMOLE Signals:
Long-duration flows (>30 min) from edge device management interface to external IP on non-standard port
Extremely low byte rate relative to duration (<10KB over >60 min)
Binary protocol on port 443 without HTTP/TLS handshake metadata
SPAWNSNAIL Signals:
SSH auth from non-management VLAN IP
Auth with key not in
authorized_keysbaselineSSH from unexpected geographic location
Alert Threshold: Any SPAWNSNAIL indicator = immediate escalation. SPAWNMOLE requires 2+ data points.
CRITICAL: SPAWN survives firmware upgrade. Do not attempt remediation via patch — engage vendor PSIRT and plan hardware replacement.
Hunt 5: DCSync from Non-Domain-Controller
Hypothesis: APT41 using domain admin credentials to replicate all AD credential material.
Core Detection Logic:
WinSec 4662: Object type = domainDNS with replication GUIDs (
1131f6ad-...DS-Replication-Get-Changes-All)Exclude: machine accounts (
$suffix) and known DC computer accountsAlert: ANY user account or non-DC machine account triggering replication
Alert Threshold: Non-DC account triggering DS-Replication-Get-Changes-All = CRITICAL. Definitive DCSync indicator.
Hunt 6: ESXi Hypervisor — Unauthorized VIB or Rogue VM
Hypothesis: BRICKSTORM persists as unauthorized VIB on ESXi hosts with network listeners and modified startup scripts.
VIB Audit:
List all VIBs, filter for
CommunitySupportedacceptance levelCompare against known-good baseline from change management
Network Listener Audit:
List all TCP/UDP listeners — any port not associated with VMware services (443, 22, 902) indicates backdoor
Attention to high-numbered ports (>10000) and port 8090 (Junction implant)
VM Audit:
Monitor for unsanctioned VM creation/deletion, especially cloning of DCs or credential vaults
Review VPXD logs for clone events outside business hours
Alert Threshold: Any unauthorized VIB = CRITICAL. Any unregistered VM = immediate investigation.
Part V — Leadership Briefing: Strategic Threat Posture
The Strategic Reality
The PRC cyber threat to your organization is not primarily about attacks — it is about persistent access for intelligence collection, potentially spanning years. The defining characteristic of China's most sophisticated operations (Salt Typhoon, Storm-0558, BRICKSTORM) is that they were active for 12–36 months before detection. You are not trying to prevent a cyberattack; you are trying to detect a nation-state intelligence operation that may already be underway.
The key insight: you don't just monitor PRC threat actors — you monitor the attack surfaces they have shifted to. When PRC operations moved from Exchange servers to edge devices to hypervisors to telecom backbone, detection had to move with them.
Three Things Leadership Must Understand
1. The traditional security stack has limited visibility into China's current tradecraft.
China's 2024–2026 approach (firmware implants, token forgery, hypervisor persistence) is specifically designed to operate below the visibility of EDR products, which run inside the OS on workstations. If the compromise is in the network device firmware (SPAWN), the Cisco router (Salt Typhoon), or the hypervisor (BRICKSTORM), your endpoint security is not looking at that attack surface.
Investment priority: Network traffic analysis (NTA) for behavioral anomalies, and edge device integrity verification programs.
2. Cloud identity is the new perimeter — and it has been compromised at the provider level.
Storm-0558 didn't need to compromise your M365 environment — they compromised Microsoft's signing key infrastructure and used it against you. Your security controls are downstream of a trust relationship with a vendor whose infrastructure was successfully penetrated.
Investment priority: Continuous access review in M365, conditional access policies that require device compliance and location constraints, and monitoring of the M365 Unified Audit Log (which requires an E5 or equivalent license — this is not optional for high-risk organizations).
3. Remediation of SPAWN requires hardware replacement, not patching.
If a SPAWN-infected device is discovered in your environment, standard patch/upgrade remediation will not work. Operational planning must account for the possibility that remediation of an edge device compromise requires physical replacement — with associated procurement lead times and service disruption.
Investment priority: Hardware replacement budgets and operational continuity planning for edge infrastructure.
Risk Prioritization by Actor
This document reflects threat intelligence through 2025. Given China's demonstrated operational tempo and adaptive tradecraft, detection signatures and hunt hypotheses should be reviewed quarterly against current CISA/NSA advisories and threat intelligence reporting.
References
2026 Annual Threat Intelligence Reports
Government & Regulatory Advisories
Campaign-Specific Vendor Reporting (2021–2026)
MITRE ATT&CK Group Profiles
Ready to see Aviatrix in action?
Get a personalized live demo walkthrough or explore our latest deep-dive cloud threat research intelligence.

