In an unprecedented joint cybersecurity advisory, 17 security agencies from 11 countries — including the United States, United Kingdom, Germany, Japan, Australia, and Canada — have confirmed that Chinese state-sponsored actors are actively compromising edge and backbone routers to maintain long-term access to sensitive networks across the globe.
The CISA AA25-239A advisory warns that attackers are exploiting known, unpatched vulnerabilities in widely deployed devices to persist below the radar — modifying router configurations, capturing traffic, and harvesting credentials without triggering traditional defenses.
And while the advisory does not explicitly confirm cloud compromise, the tactics it describes — credential harvesting, lateral movement from edge infrastructure, and the use of trusted services to mask exfiltration — are exactly how Chinese APTs have pivoted into cloud and SaaS environments in prior campaigns.
Hijacking Routers — and the Trust They Carry
Attackers are actively exploiting vulnerabilities in platforms like:
Once inside, attackers modify Access Control Lists (ACLs), enable Generic Routing Encapsulation (GRE) or IPsec tunnels, and configure covert SSH or web services on high ports. They also use packet capture (PCAP) tools to sniff network traffic and exploit Simple Network Management Protocol (SNMP) and Terminal Access Controller Access-Control System Plus (TACACS+) to escalate access and discover additional infrastructure.
How This Enables Cloud Infiltration
The advisory documents credential harvesting and lateral movement from infrastructure — both well-known tactics that enable attackers to move from routers into cloud environments.
While the report doesn’t explicitly say “Chinese APTs compromised AWS or Azure,” it describes the exact conditions for such a pivot:
Long-term access to infrastructure trust paths
Harvested credentials and authentication flows
Tunnels and ACLs allowing stealthy movement into connected systems
These tactics align with previously documented campaigns where Chinese APTs gained infrastructure access and then infiltrated cloud control planes and SaaS applications.
Real-World Example: APT40’s Router-to-Cloud Infiltration
In 2021–2022, APT40, a Chinese state-sponsored threat group, exploited vulnerable routers and VPNs, harvested credentials, and gained access to Microsoft 365 and other SaaS platforms using valid logins.
They disguised traffic through trusted infrastructure and tunnels — mirroring the tactics seen in AA25-239A.
This proves that infrastructure compromise is not the end — it’s the beginning of cloud infiltration.
Why Traditional Tools Don’t Catch This
Security controls built for endpoints and posture fall short when the attack is living inside the infrastructure.
Endpoint Detection and Response (EDR) isn’t present on routers
Next-Generation Firewalls (NGFWs) don’t detect internal ACL manipulation or GRE/IPsec abuse
Security Information and Event Management (SIEM) tools can’t correlate router behavior with credential harvesting
Zero Trust architectures often lack enforcement between infrastructure and cloud workloads
By the time cloud compromise occurs, the attacker is using valid credentials and established tunnels from trusted devices.
How Aviatrix CNSF Closes the Gap
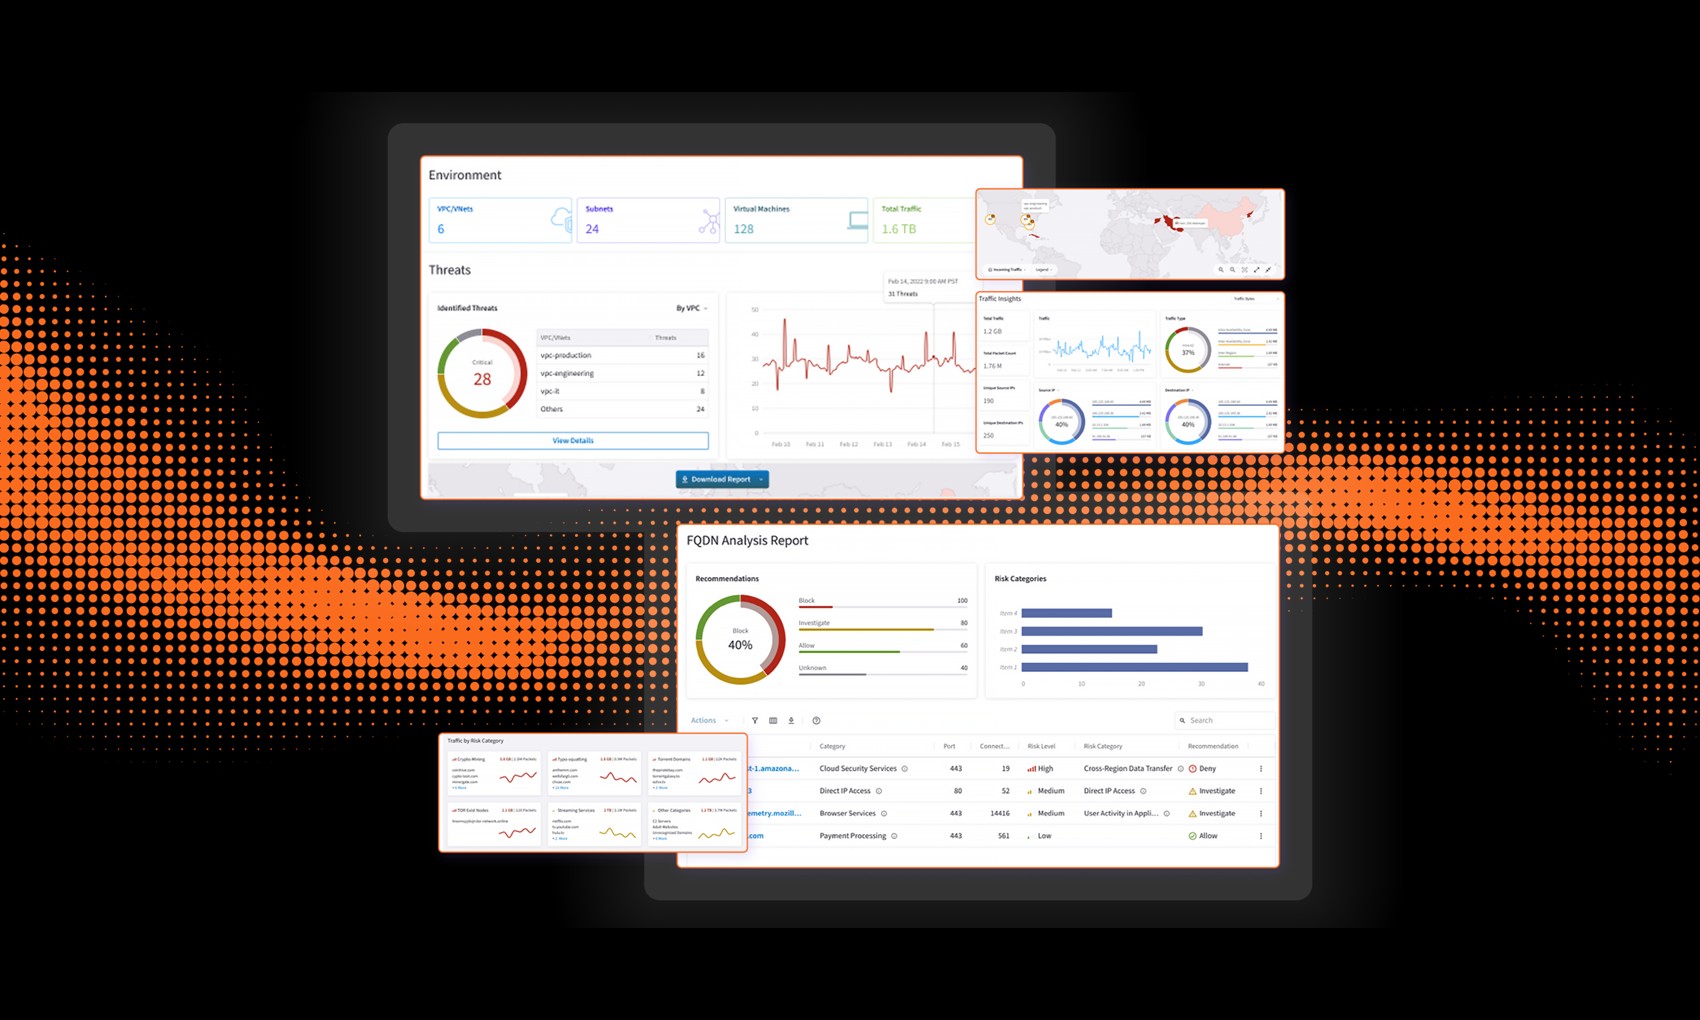
The Aviatrix Cloud Network Security Fabric (CNSF) delivers real-time enforcement and visibility where traditional tools fail — at the runtime infrastructure layer.
With CNSF, organizations gain:
Inline visibility into edge, inter-region, and inter-cloud traffic
Detection of ACL anomalies, tunneling behavior, and covert service exposure
Microsegmentation that blocks identity-based pivots into cloud VPCs or SaaS
Threat chain mapping through CoPilot, our observability and analytics platform
Flow + DNS + telemetry correlation to detect credential-based escalation
No agents to manage. No deep packet dependency. Just zero Ttust enforcement built into the fabric of your cloud and network infrastructure.
What It Means for Compliance
This attack campaign exposes critical visibility and control gaps across regulatory frameworks:
Framework | Impact |
CISA ZTMM 2.0 | Fails segmentation, enforcement, and visibility at infrastructure |
EO 14028 | Violates APT detection mandates for federal contractors |
HIPAA 2025 | Exposes PHI in motion at under-secured network edges |
PCI DSS 4.0 | Enables unmonitored paths for cardholder data |
NIS2 / DORA | Lacks runtime observability for regulated critical infrastructure |
What You Can Do Now
You don’t need new hardware — you need visibility and enforcement in the network fabric.
👉 Talk to a security specialist
📚 Sources (with full URLs)
CISA Advisory AA25-239A: https://www.cisa.gov/news-events/cybersecurity-advisories/aa25-239a
NVD CVE‑2024‑21887 (Ivanti): https://nvd.nist.gov/vuln/detail/CVE-2024-21887
NVD CVE‑2024‑3400 (Palo Alto): https://nvd.nist.gov/vuln/detail/CVE-2024-3400
NVD CVE‑2023‑20198 (Cisco IOS XE): https://nvd.nist.gov/vuln/detail/CVE-2023-20198
APT40 Advisory (Australia): https://www.cyber.gov.au/about-us/view-all-content/alerts-and-advisories/apt40-advisory-prc-mss-tradecraft-in-action
IBM X-Force Threat Intelligence Index 2024: https://www.ibm.com/reports/threat-intelligence
Verizon DBIR 2025: https://www.verizon.com/business/resources/reports/dbir/
Ready to see Aviatrix in action?
Get a personalized live demo walkthrough or explore our latest deep-dive cloud threat research intelligence.
Gartner Strategic Roadmap for Zero Trust Security Programs 2025 Report
Download and gain actionable insights to advance your cloud security strategy.