
The Containment Platform for Every Cloud Workload
Realize NIST & CISA's Zero Trust goals. CNSF is the embedded enforcement fabric that makes Zero Trust a reality.
When prevention fails and detection is too slow, containment decides whether the incident becomes a breach.
Your Largest Attack Surface Isn't at the Edge. It's Between Workloads. The Containment Platform governs every workload, every path.
The cloud vaporized the traditional perimeter. This created a new battleground: the unmonitored, implicitly trusted pathways between your workloads. Attackers now bypass edge defenses and move laterally to exfiltrate data undetected.

Architectural Complexity
92% of organizations are multi-cloud, each with unique, incompatible security tools. Your apps are no longer monolithic, but ephemeral containers and functions.

"Shadow AI" & K8s Risk
The rush to adopt AI creates "Shadow AI" agents that bypass old controls. Kubernetes' complexity also leaves critical risks, like lateral threat movement, overlooked.

Ephemeral Workloads
Applications are no longer monolithic. They are transient ecosystems of containers and functions that are created and destroyed in seconds.
Chokepoint Security vs. Containment Architecture
A chokepoint governs the traffic that routes through it. Communication Governance governs every path.
Transit
Firewall
Transit
Firewall
Detailed Comparison
| Dimension | Chokepoint Security | Containment Architecture |
|---|---|---|
| Enforcement Point | Central transit firewall | Every workload |
| K8s Pod Egress | Invisible | Governed |
| Serverless Functions | Invisible | Governed |
| East-West Traffic | Depends on routing | Governed |
| Policy Propagation | Hours/days per device | Subsecond, universal |
| Blast Radius | Network-wide | Single workload |
"The distinction is not 'egress filtering vs. no egress filtering.' The distinction is where the enforcement lives."
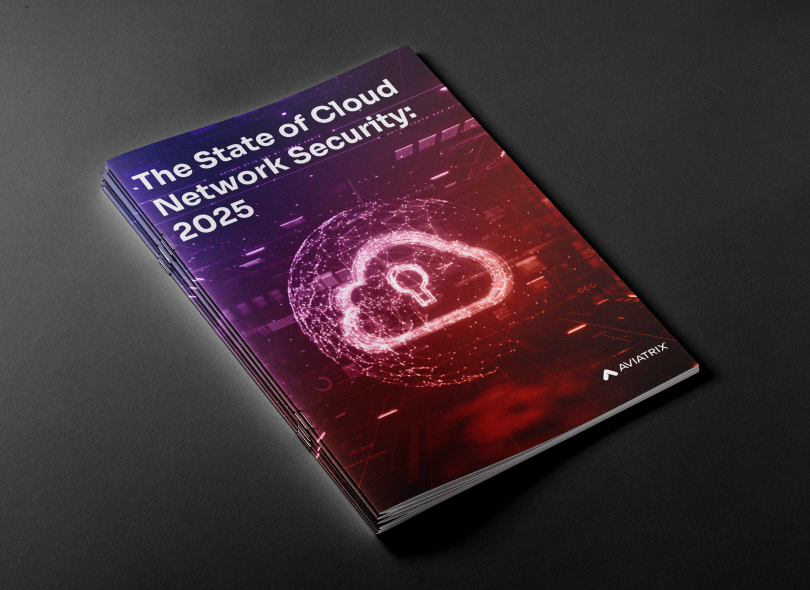
Inside Real Breaches: How CNSF Stops Lateral Movement and Data Theft
Learn from MGM Resorts and MOVEit: attackers used social engineering and supply chain exploits to move east-west and steal data. The whitepaper shows how Cloud Native Security Fabric blocks lateral movement, contains blast radius, and stops unintentional data leakage.
Containment, Built Into the Fabric
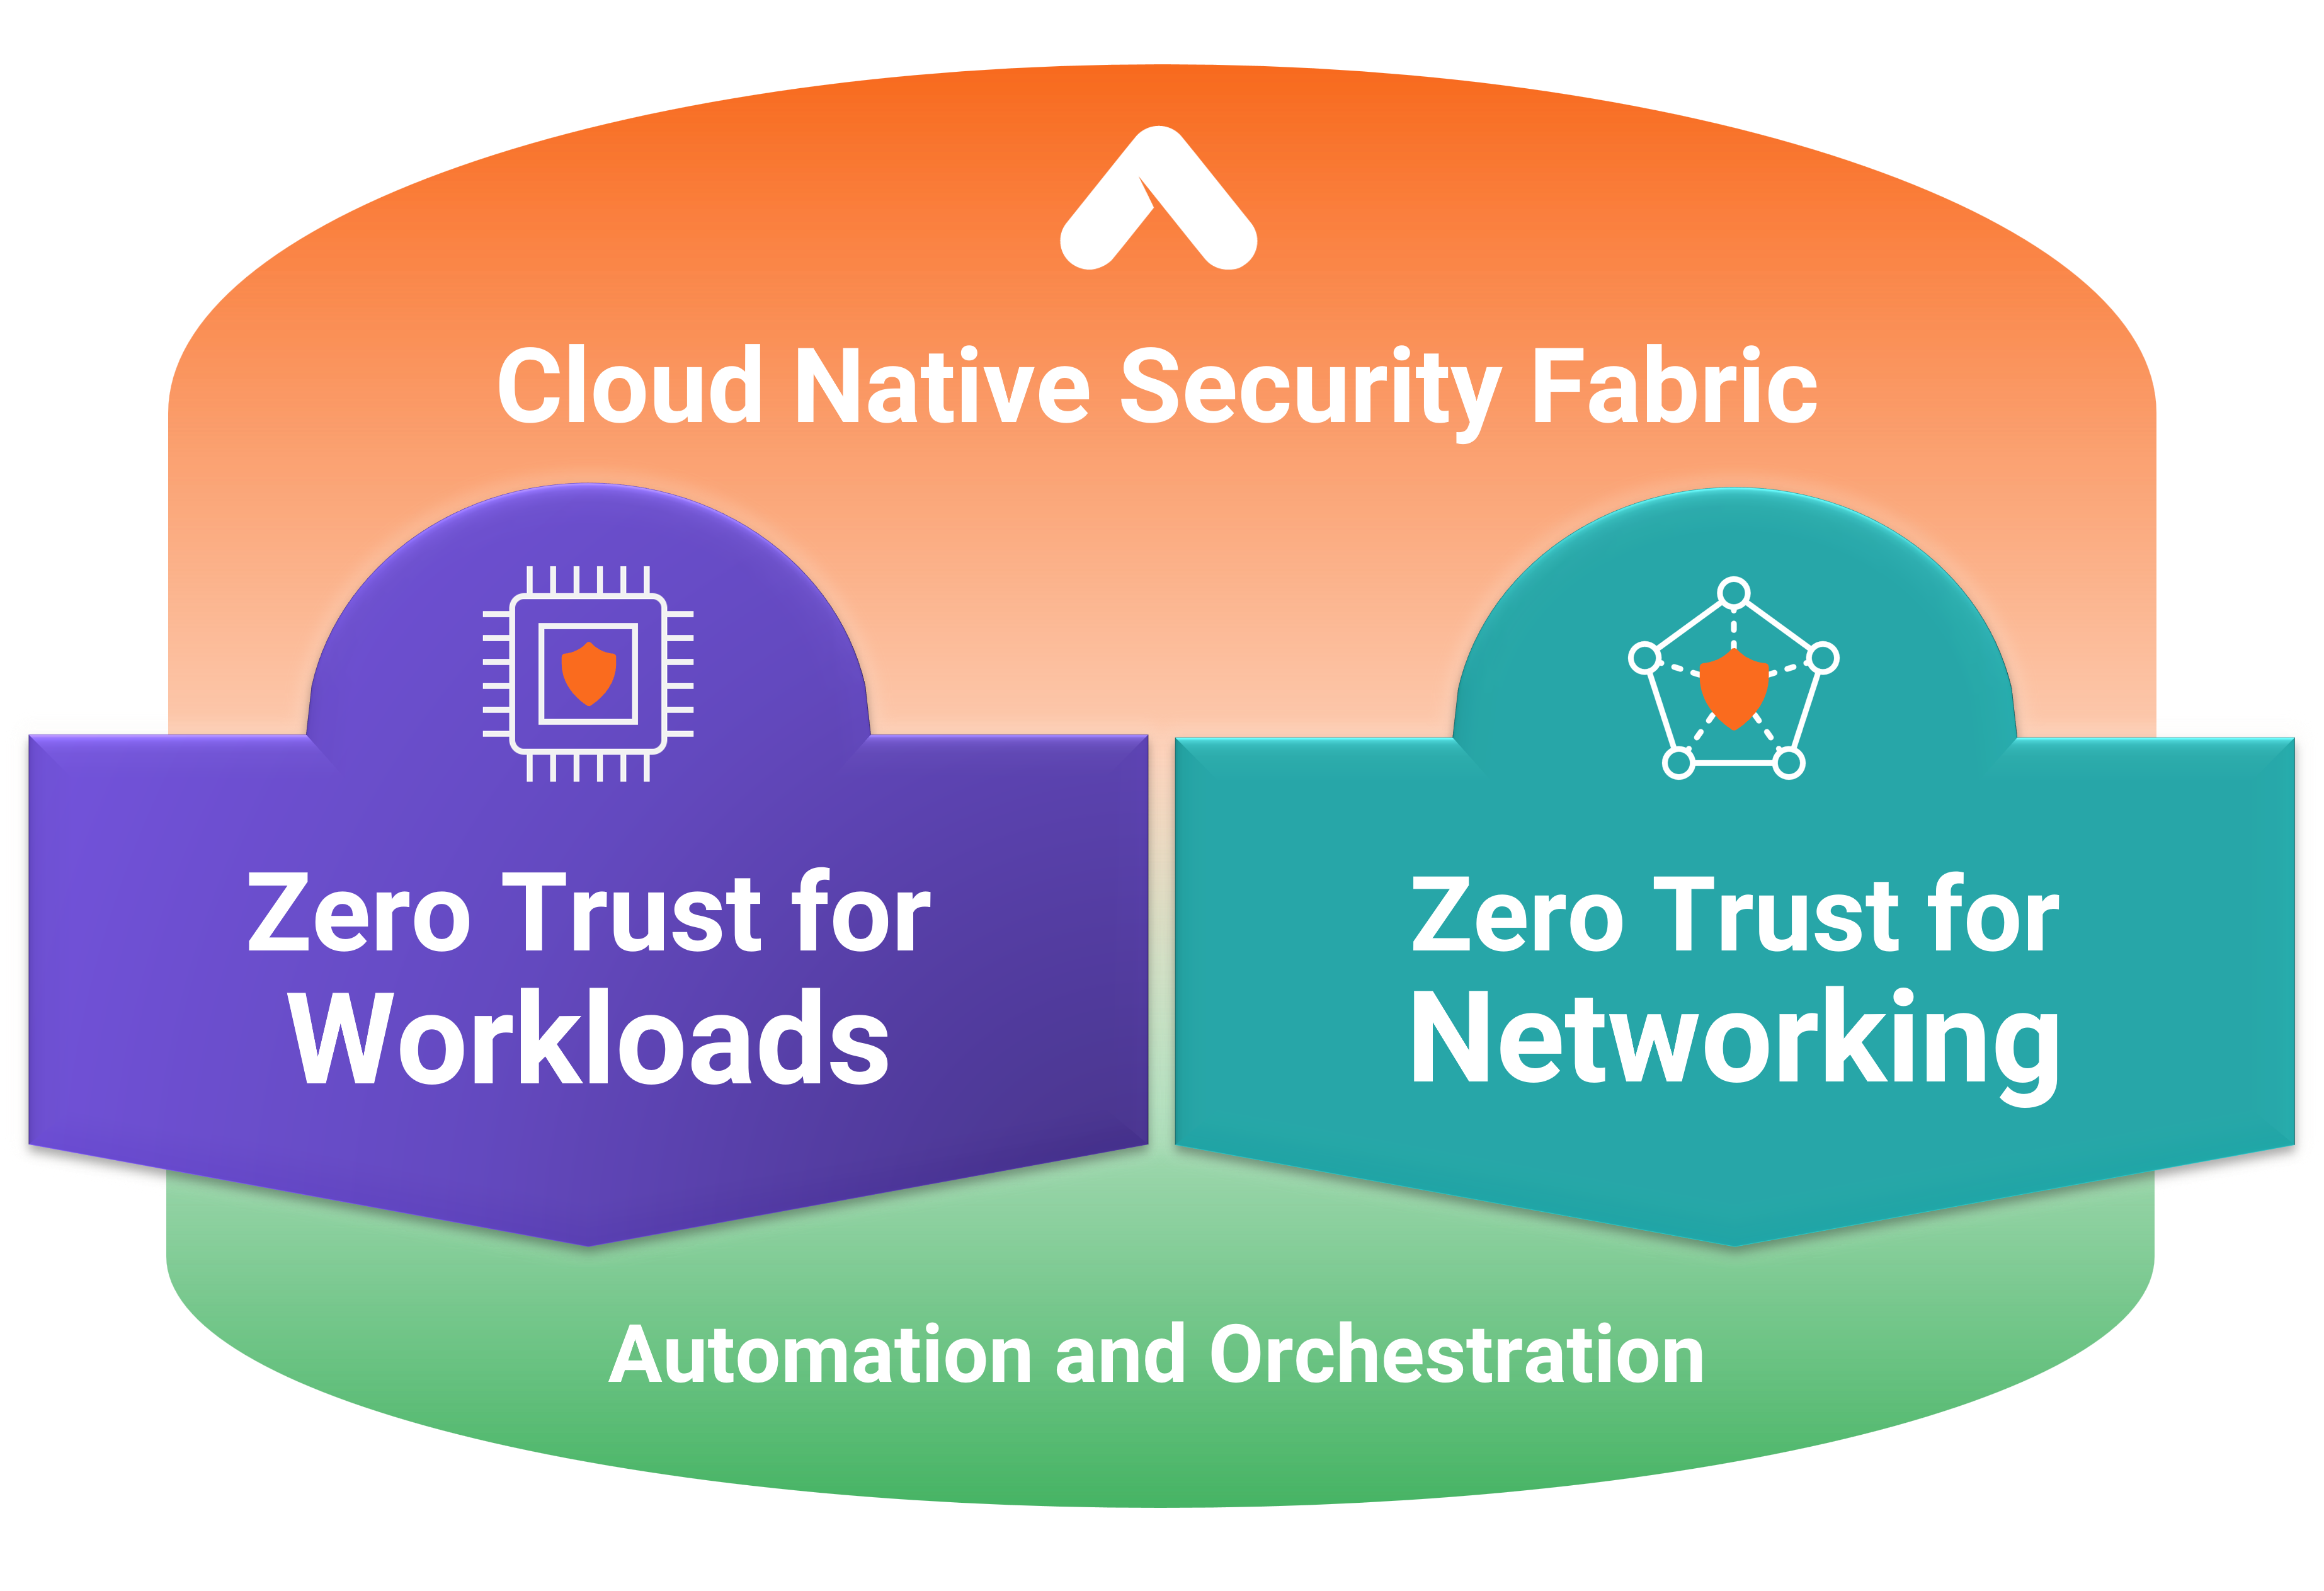
Instead of bolting security onto the edge, Aviatrix Cloud Native Security Fabric™(CNSF) weaves runtime enforcement into the cloud fabric. In-line points broker least-privilege connections, while one control plane applies consistent policy everywhere.
- AVIATRIX CLOUD NATIVE SECURITY FABRIC (CNSF)
Here’s How CNSF Changes Cloud Security:
- Embedded
Policies live inside your cloud—not the edge.
- Dynamic
Segmentation moves with workloads automatically.
- Agentless
No agents, no middleboxes, no bottlenecks.
- Real-time
Every session verified instantly, with no lag.
- Pervasive
Unified protection across multicloud, on-prem, edge, containers, functions and AI workloads with consistent security.
- Transparent
Developer-friendly. Operates below the app layer—no code changes or DevOps friction.
- Frictionless
Strong controls with negligible latency.
Zero Trust for Workloads
Aviatrix Zero Trust for Workloads secures workload-to-workload and workload-to-internet traffic in real time. Deployed within existing cloud architectures, it does not require network redesign.
Zero Trust for Networking
Aviatrix Zero Trust for Networking, built on High-Performance Encryption (HPE) secures the fabric itself—ensuring that every connection is encrypted, auditable, and performance-optimized.
Minimize Your Cloud Breach Risk
CNSF is the missing "how" for Zero Trust, delivering the implementation for NIST & CISA goals . As an in-line enforcement fabric, it provides measurable outcomes: fewer breaches, consistent policy, and simpler compliance.
Make Your Security Stack Stronger with Cloud Native Control
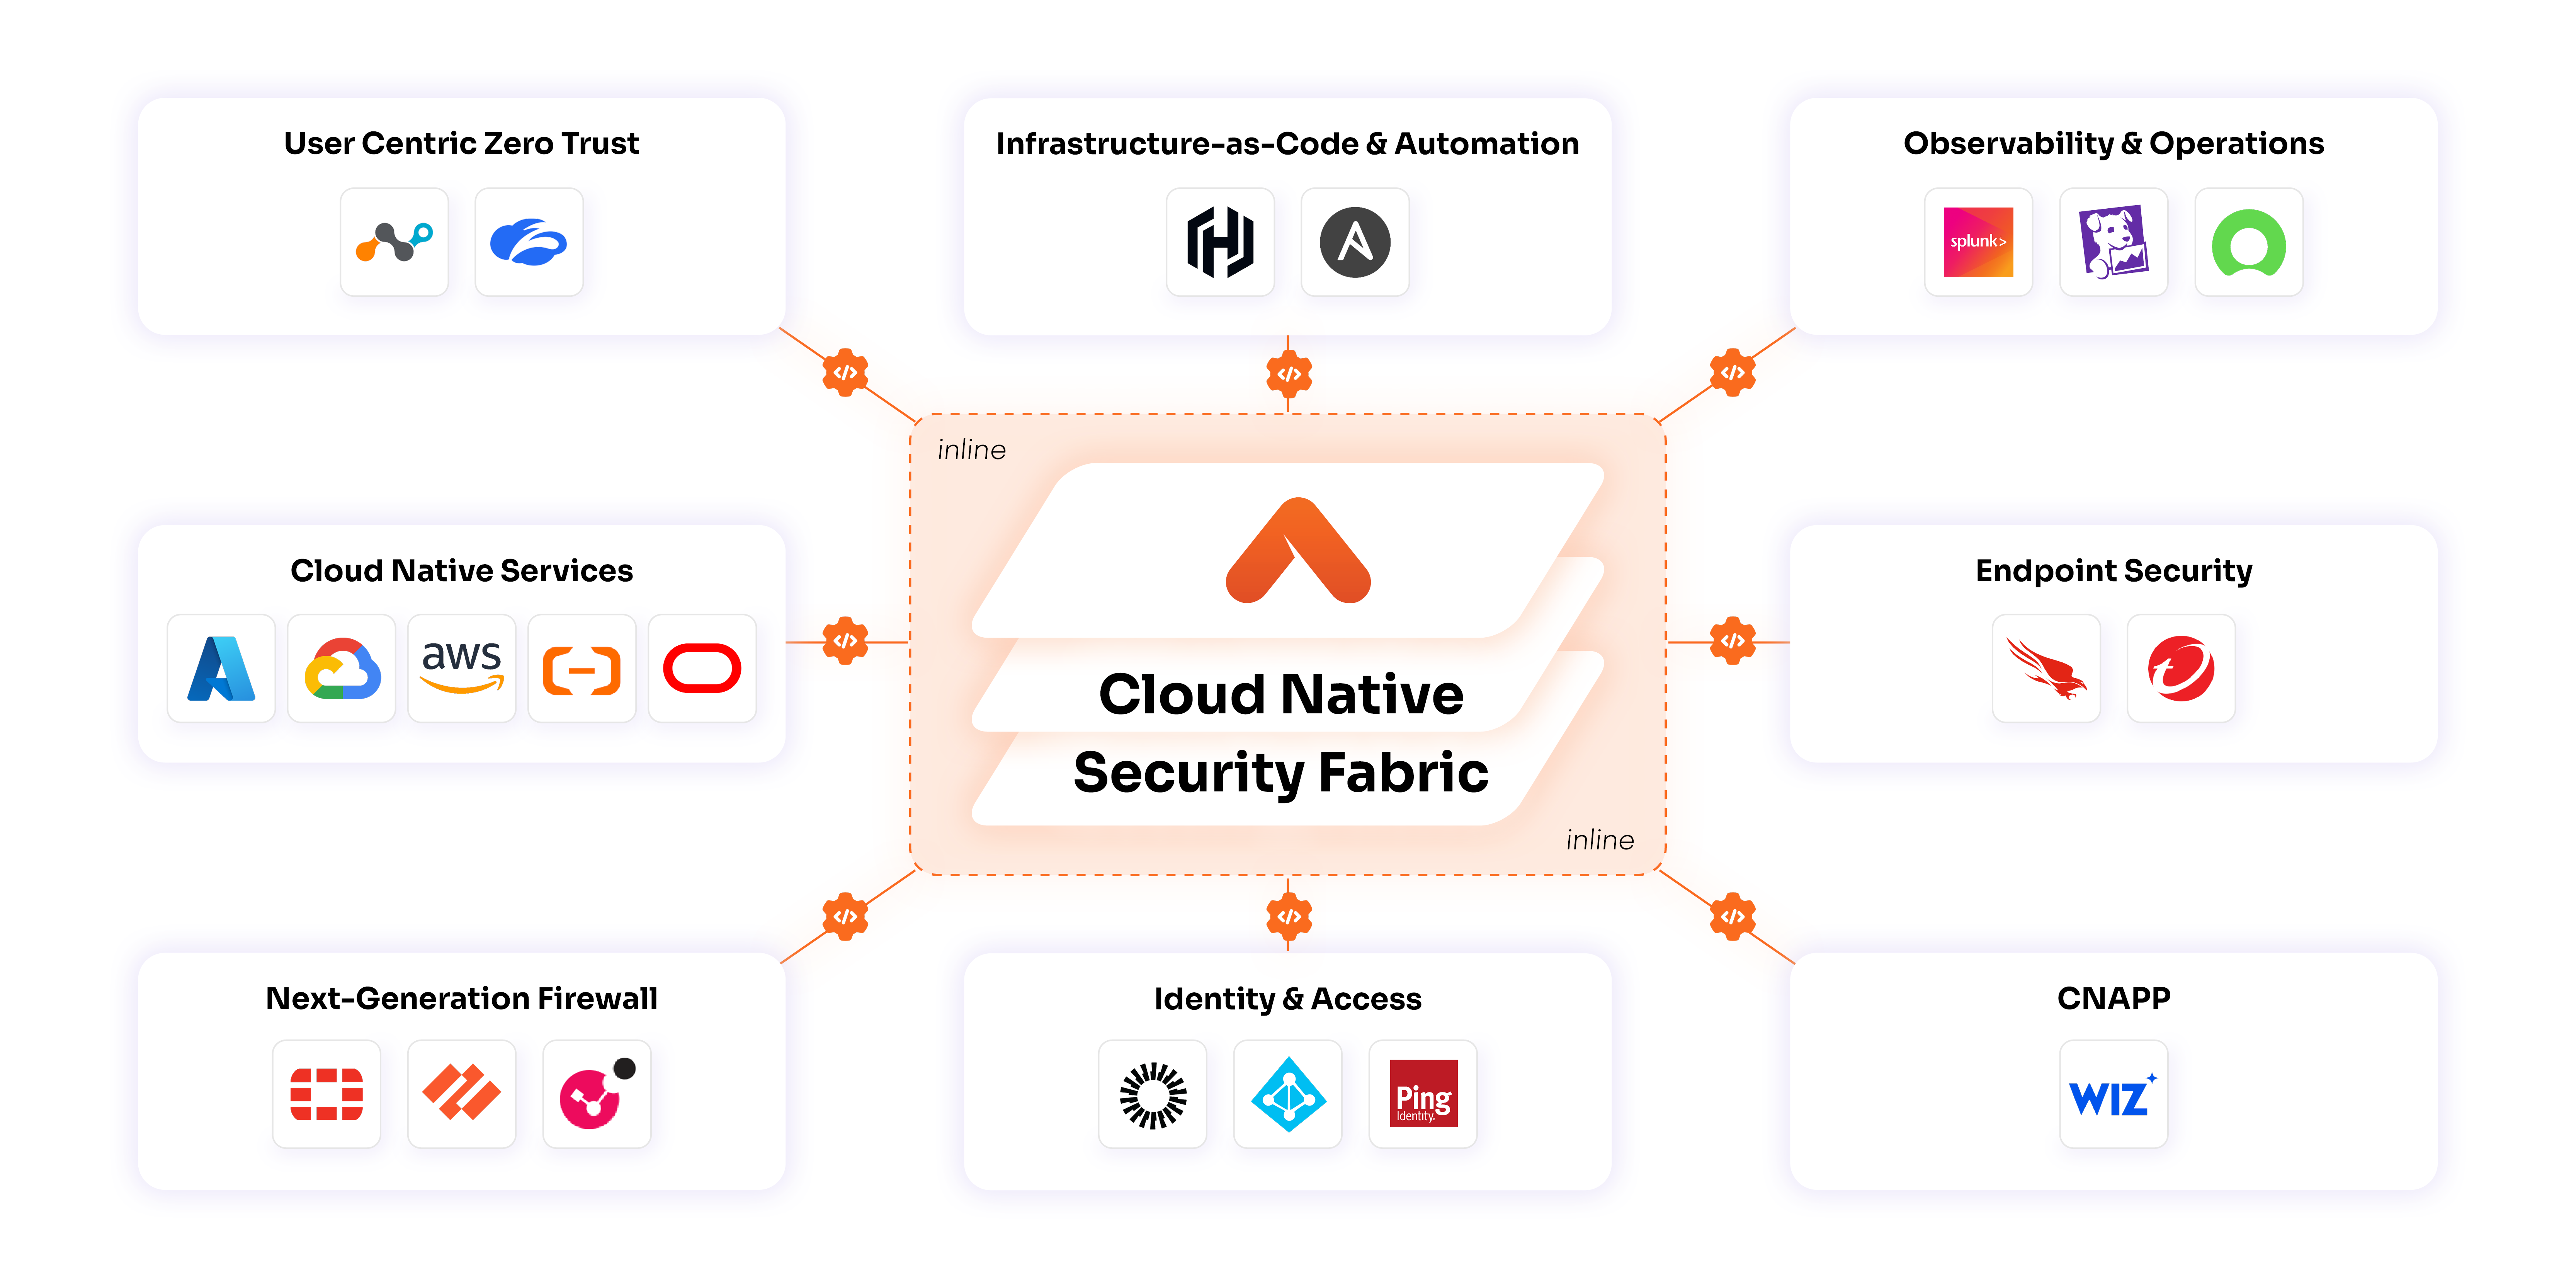
CNSF works better with the ecosystem you already have, amplifying investments and extending zero trust end-to-end.

Amplifying Third-Party Insights
Turn alerts from Wiz, CrowdStrike, and others into real-time network enforcement.

Extending Zero Trust Beyond Users
Pair with Zscaler or Cloudflare: they secure user access, CNSF secures app-to-app traffic inside the cloud.

Coexisting with NGFWs & Cloud Services
Work alongside Palo Alto and native cloud services, extending protection beyond perimeter enforcement.
Including 10% of the Fortune 500
500+ Enterprises Secure Cloud and AI with Aviatrix





Recognition That Reflects Real Impact
Awards and analyst validation highlight Aviatrix’s role in shaping the future of cloud security. These honors underscore a commitment to innovation, zero trust, and practical solutions that help enterprises secure transformation with confidence.
Award-Winning Innovation
Recognized with the 2025 Cloud Security Excellence Award for embedding zero trust into the cloud fabric.
Industry Accolades
Named among North America’s fastest-growing tech companies (Deloitte Technology Fast 500™).
Thought Leadership
Aligned with NIST and CISA frameworks, sharing insights that help shape the future of cloud security.

See Aviatrix CNSF in action.
Request a demo and discover how CNSF secures your cloud end-to-end. Explore use cases, assess your posture, and eliminate blind spots while accelerating initiatives.
