The breach isn’t the problem. The spread is. →Free Assessment

STRUCTURED THREAT INTELLIGENCE FOR THE CLOUD COMMUNITY

Aviatrix Threat Research Center

Cloud breaches are accelerating — across identities, workloads, supply chains, and cloud-native services. In the Containment Era, understanding how a breach unfolds is how you architect to stop it.

The Aviatrix Threat Research Center provides security teams with:

  • A structured understanding of how breaches unfold — kill chain, ATT&CK techniques, CVEs, and IOCs in a consistent format.
  • What attackers exploited, and which enforcement gaps let them move.
  • Where workload-level controls would have broken the attack chain — including paths that posture tools and endpoint detection don't model.
Kill Chain Coverage
ATT&CK Mapped
Real-World IOCs
Graphic-for-second-Salt-Typhoon-blog-2
Threat ReportsLive Intelligence

Recent Breaches, Security Incidents & Vulnerabilities

A unified view of real-world cloud threats — combining AI-powered analysis, security research, and expert perspectives through a consistent, cloud-specific framework.

AI-Powered Threat Analysis

Agentic AI that analyzes real-world attacks — across security incidents, breaches, and exploited vulnerabilities — to produce structured, actionable intelligence.

Browse by Industry
AccountingAerospaceAerospace/AviationAgricultureAirlines/AviationAnimationApparel/FashionArchitecture/PlanningArtificial IntelligenceArtificial Intelligence/Machine LearningArts/CraftsAutomotiveAviation/AerospaceBanking/MortgageBiotechnology/GreentechBlockchain/CryptocurrencyBroadcast MediaBroadcasting MediaBroadcasting/MediaBuilding MaterialsBusiness Supplies/EquipmentCapital Markets/Hedge Fund/Private EquityChemicalChemicalsCivic/Social OrganizationCivil EngineeringCloud ComputingCloud Computing/SaaSCloud ServicesCommercial FacilitiesCommercial Real EstateComputer GamesComputer HardwareComputer NetworkingComputer Software/EngineeringComputer/Network SecurityConstructionConsultingConsumer ElectronicsConsumer GoodsConsumer ServicesCosmeticsCosmeticsCritical ManufacturingCryptocurrenciesCryptocurrencyCustomer ServicesCybersecurityDairyDating/Personal ServicesDating/Social PlatformsDefense/SpaceDesignE-LearningEducation ManagementElectrical/Electronic ManufacturingEmergency ServicesEnergyEnergy/Oil/Solar/GreentechEntertainment/Movie ProductionEnvironmental ServicesEvents ServicesExecutive OfficeFacilities ServicesFarmingFashion/ApparelFinancial ServicesFine ArtFisheryFood ProductionFood/BeveragesFortune 500 companiesFranchisingFundraisingGambling/CasinosGamingGaming/CasinosGovernment AdministrationGovernment FacilitiesGovernment RelationsGraphic Design/Web DesignHealth Care / Life SciencesHealthcareHigher Education/AcadamiaHospitalityHospitalsHuman Resources/HRImport/ExportIndividual/Family ServicesIndustrial AutomationInformation ServicesInformation Technology/ITInsuranceInternational AffairsInternational Trade/DevelopmentInternetInvestment Banking/VentureInvestment Management/Hedge Fund/Private EquityJudiciaryLaw EnforcementLaw Practice/Law FirmsLegal ServicesLegislative OfficeLeisure/TravelLogistics/ProcurementLuxury Goods/JewelryMachineryManagement ConsultingManufacturingMaritimeMarketing/Advertising/SalesMechanical or Industrial EngineeringMedia ProductionMedical EquipmentMedical PracticeMilitary IndustryMining/MetalsMobileMuseums/InstitutionsMusicNewspapers/JournalismNon-Profit/VolunteeringOil/Energy/Solar/GreentechOnline PublishingOutsourcing/OffshoringPackage/Freight DeliveryParkingPharmaceuticalsPhilanthropyPhotographyPlasticsPolitical OrganizationPrimary/Secondary EducationProfessional ServicesProfessional TrainingPublic Relations/PRPublic SafetyPublishing IndustryRailroad ManufactureReal Estate/MortgageRecreational Facilities/ServicesReligious InstitutionsRenewables/EnvironmentResearch IndustryRestaurantsRetail IndustryRoboticsRural HealthcareSecurity/InvestigationsSemiconductorsShipbuildingSocial Media/InternetSporting GoodsSportsStaffing/RecruitingSupermarketsTechnologyTechnology/ITTelecommunicationsThink TanksToys and GamesTransportationTravel/TourismTrucking/FreightUtilitiesVenture Capital/VCWarehousingWater and Waste ManagementWater and WastewaterWater and Wastewater SystemsWater and Wastewater TreatmentWater TreatmentWater, Waste, Steam, and Air Conditioning ServicesWater/Waste ManagementWater/WastewaterWater/Wastewater ManagementWater/Wastewater/UtilitiesWholesaleWine/SpiritsWirelessWriting/Editing

Displaying 6505 to 6516 of 6710 threat reports

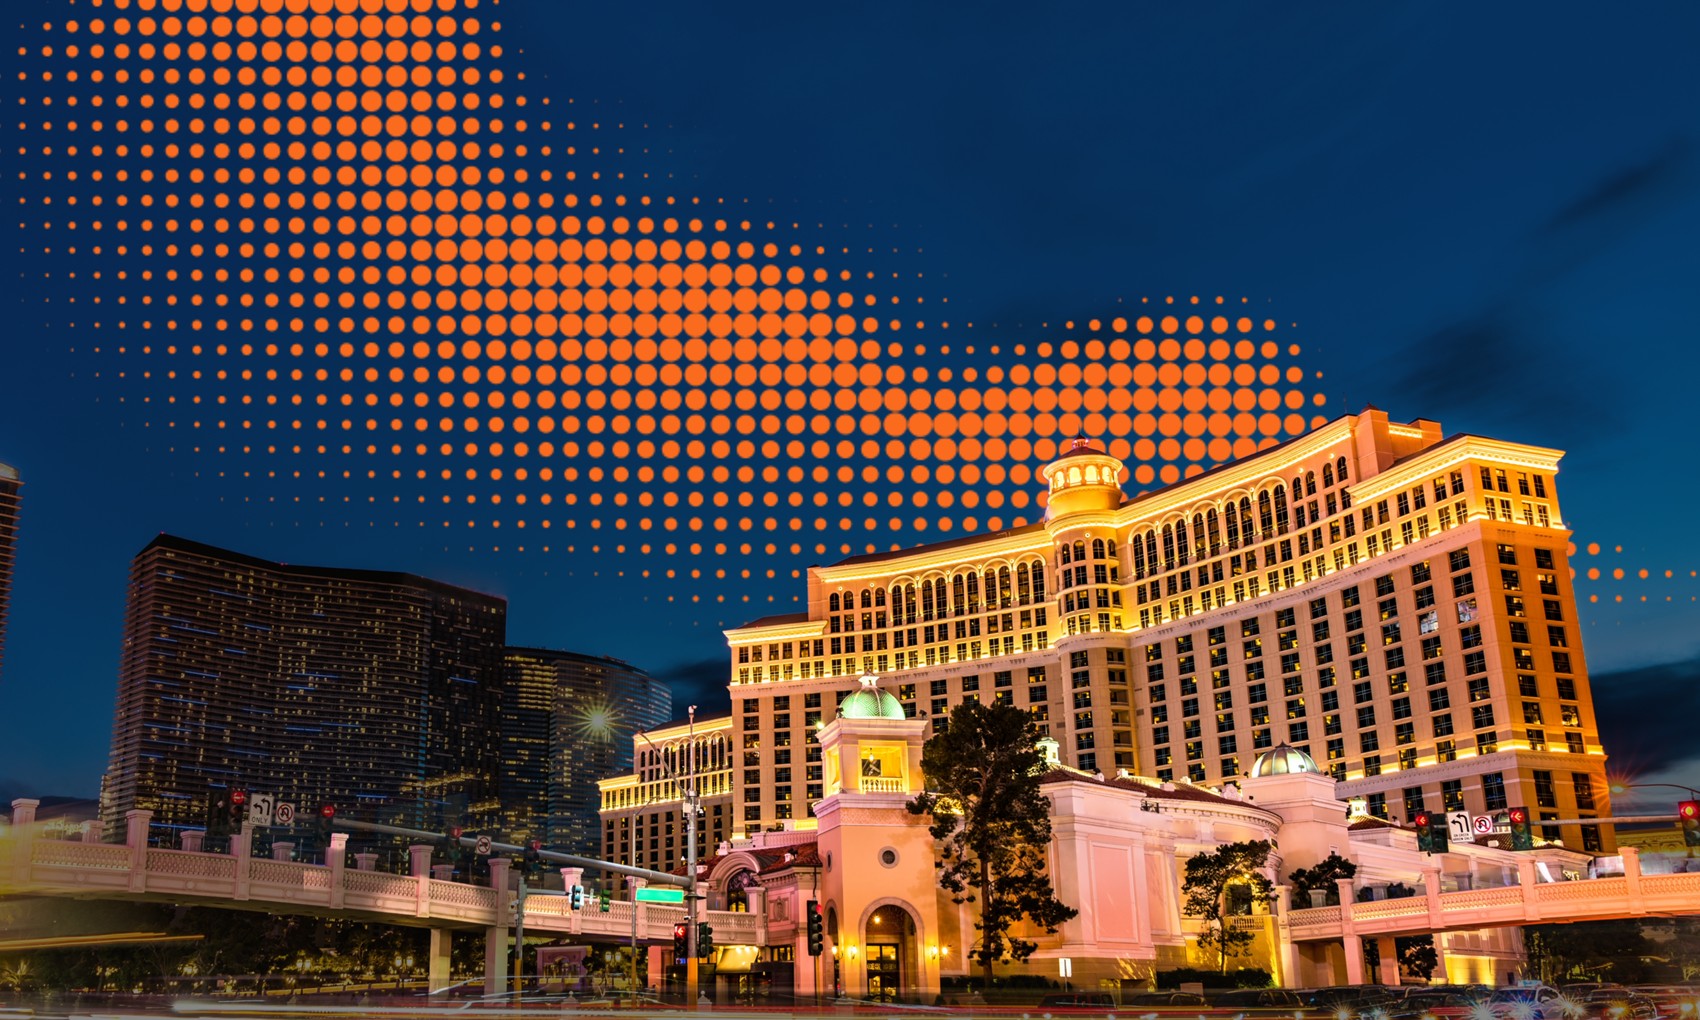
Teen Arrested in 2023 Las Vegas Casino Ransomware Attacks Linked to Scattered Spider
Gambling/Casinos9 months ago

Teen Arrested in 2023 Las Vegas Casino Ransomware Attacks Linked to Scattered Spider

In late 2023, Las Vegas casinos suffered major cyberattacks attributed to the Scattered Spider threat group, resulting in widespread operational disruption. The attacks targeted MGM Resorts International and Caesars Entertainment, leveraging sophisticated social engineering and phishing tactics to gain network access, move laterally, and ultimately extort ransom payments. MGM reported losses exceeding $100 million, while Caesars reportedly paid $15 million to mitigate risks. In June 2024, a local teenage suspect was arrested in connection to these events, highlighting the involvement of young, native English-speaking cybercriminals and a broader international law enforcement response. This incident exemplifies the increasing prevalence of highly organized, technology-savvy ransomware and extortion campaigns that rely on social engineering and identity-centric attack vectors. Organizations across industries face rising risks as threat groups adopt coordinated, multifaceted tactics to exploit internal and hybrid cloud environments.

High impact

Kill Chain

ICInitial Compromise(high)
PEPrivilege Escalation(medium)
LMLateral Movement(medium)
C&CCommand & Control(medium)
EExfiltration(medium)
IImpact(high)
Read report
Secret Service Disrupts Extensive NYC Telecom Threat Targeting UN Assembly
Telecommunications9 months ago

Secret Service Disrupts Extensive NYC Telecom Threat Targeting UN Assembly

In September 2025, the U.S. Secret Service disrupted a sophisticated illicit telecom infrastructure in the New York City area, uncovering more than 300 servers and over 100,000 SIM cards located near the United Nations General Assembly. The operation identified a network enabling encrypted, anonymous communications allegedly used by foreign actors, criminals, and potentially threat groups to coordinate activities and transmit assassination threats. Investigators warned that the scale of the system posed significant risk, including the theoretical ability to disable cellular networks and disrupt critical communications during high-security events. This incident highlights rising risks of criminal and nation-state actors leveraging physical telecom infrastructure to subvert detection, illustrating how sophisticated SIM farms and server farms can facilitate large-scale anonymity and attacks. The operation underscores heightened scrutiny on telecom supply chain security during high-profile events and the need for robust infrastructure monitoring.

High impact

Kill Chain

ICInitial Compromise(medium)
PEPrivilege Escalation(low)
LMLateral Movement(medium)
C&CCommand & Control(high)
EExfiltration(medium)
IImpact(high)
Read report
AT&T 2023: How Salt Typhoon Changed the APT Playbook
Telecommunications9 months ago

AT&T 2023: How Salt Typhoon Changed the APT Playbook

In 2023, the telecommunications giant AT&T was targeted by the advanced persistent threat group Salt Typhoon, which launched a sophisticated campaign exploiting unconventional vulnerabilities. Unlike conventional attacks, Salt Typhoon focused on endpoints lacking robust detection and response (EDR), hunted for network blind spots with minimal logging, and engaged in 'living off the land' attacks—leveraging legitimate administrative tools to evade detection and persist inside networks. This multi-pronged methodology enabled deep network infiltration before discovery, ultimately jeopardizing sensitive data and service availability across AT&T’s infrastructure. Following the breach, the company reported the threat group was successfully evicted from its systems. This incident has set a precedent, with numerous threat actors now adopting Salt Typhoon’s tactics to bypass traditional security controls. The breach highlights an urgent need for organizations to enhance monitoring, bolster endpoint visibility across all platforms, and adapt defenses for evolving attacker methodologies in critical infrastructure sectors.

Medium impact

Kill Chain

ICInitial Compromise(medium)
PEPrivilege Escalation(low)
LMLateral Movement(medium)
C&CCommand & Control(medium)
EExfiltration(medium)
IImpact(medium)
Read report
Steam’s Platform Breached: BlockBlasters Game Used for Massive 2025 Crypto Theft
Computer Games9 months ago

Steam’s Platform Breached: BlockBlasters Game Used for Massive 2025 Crypto Theft

In September 2025, a verified Steam game, BlockBlasters, was discovered to have been weaponized to steal cryptocurrency from users, including a content creator raising money for cancer treatment. Initially benign, the game was compromised on August 30 with a cryptodrainer component that harvested Steam credentials, IP addresses, and ultimately drained victims’ digital wallets. Attackers targeted high-value accounts sourced from social media, using a mix of batch scripts, Python backdoors, and StealC payloads, leading to an estimated $150,000 in theft across hundreds of accounts. At least one streamer lost $32,000 in funds intended for lifesaving care. This incident exemplifies the growing threat of supply-chain and platform abuse, with attackers leveraging trusted app marketplaces to deliver infostealers. The BlockBlasters case underscores the urgent need for advanced egress security, anomaly detection, and zero trust controls, as attackers increasingly exploit digital trust and social media to orchestrate high-impact thefts.

High impact

Kill Chain

ICInitial Compromise(high)
PEPrivilege Escalation(medium)
LMLateral Movement(low)
C&CCommand & Control(high)
EExfiltration(high)
IImpact(high)
Read report
2025's Multichannel Phishing Campaigns: The End of Email-Only Defense
Financial Services9 months ago

2025's Multichannel Phishing Campaigns: The End of Email-Only Defense

In September 2025, organizations experienced a surge of sophisticated credential harvesting attacks that moved beyond traditional email phishing, utilizing instant messaging, social media, and malicious advertising channels. Attackers deployed advanced Attacker-in-the-Middle (AiTM) phishing kits and leveraged compromised accounts, cloned login pages, and rapid domain rotation to evade both detection and remediation. Case studies included targeted spear-phishing via LinkedIn and malvertising on Google Search, resulting in high-value session theft and lateral account compromise. These attacks not only bypassed email security but exploited any channel where business users could be reached, often leading to the breach of core cloud platforms and widespread internal access. This campaign marks a critical evolution in attacker tactics, underlining that perimeter-focused and email-only defenses are insufficient. The surge in non-email phishing brings new urgency for organizations to secure east-west traffic, implement zero trust segmentation, and enhance visibility across all cloud and SaaS environments.

Low impact

Kill Chain

ICInitial Compromise(high)
PEPrivilege Escalation(medium)
LMLateral Movement(medium)
C&CCommand & Control(medium)
EExfiltration(medium)
IImpact(low)
Read report
Fake Password Managers Spread AMOS Malware on Mac: The 2025 LastPass Incident

Fake Password Managers Spread AMOS Malware on Mac: The 2025 LastPass Incident

In September 2025, LastPass reported an ongoing malware campaign targeting macOS users with fake password managers distributed through fraudulent GitHub repositories and deceptive SEO-optimized links. The attackers impersonated over 100 popular software products—including LastPass, 1Password, Dropbox, and others—using build-your-own repositories that redirected victims to install scripts containing the Atomic (AMOS) infostealer malware. Victims were instructed to run shell commands that downloaded backdoored payloads, risking credential theft, data exfiltration, and sustained system compromise. The campaign employed automated methods for rapid replication and evasive takedown resistance. This incident underscores a surge in supply chain and social engineering attacks using open platforms and SEO abuse, highlighting the persistent vulnerabilities in software distribution channels for macOS. It demonstrates attackers' growing sophistication in exploiting user trust and platform discoverability to deploy credential-stealing malware at scale.

Medium impact

Kill Chain

ICInitial Compromise(high)
PEPrivilege Escalation(medium)
LMLateral Movement(low)
C&CCommand & Control(medium)
EExfiltration(high)
IImpact(medium)
Read report
EDR-Freeze: Novel Windows WER Technique Suspends EDR and Antivirus Tools
Financial Services9 months ago

EDR-Freeze: Novel Windows WER Technique Suspends EDR and Antivirus Tools

In September 2025, a security researcher revealed a novel user-mode evasion technique leveraging Windows Error Reporting (WER) to suspend the operation of Endpoint Detection & Response (EDR) and antivirus software. The proof-of-concept tool, EDR-Freeze, exploits a race condition by combining the WerFaultSecure component with the MiniDumpWriteDump API. Attackers can indefinitely freeze security processes by suspending WerFaultSecure precisely as it is executing a memory dump of the target, effectively leaving EDR or AV tools inert without requiring kernel-level vulnerabilities. This design weakness bypasses typical Bring Your Own Vulnerable Driver (BYOVD) defences and leaves minimal forensic evidence. This incident underscores the increasing sophistication of EDR evasion by cyber adversaries, who are rapidly adopting stealthy, native Windows attack chains. Organizations must adapt detection and monitoring practices to keep pace as user-mode bypasses erode longstanding layers of endpoint protection. The wider prevalence of such techniques signals a strategic shift in attacker tradecraft and compels a reassessment of endpoint hardening and response automation.

Medium impact

Kill Chain

ICInitial Compromise(medium)
PEPrivilege Escalation(high)
LMLateral Movement(medium)
C&CCommand & Control(low)
EExfiltration(low)
IImpact(medium)
Read report
Stellantis 2024 Salesforce Supplier Breach: Lessons on Third-Party SaaS Risk
Automotive9 months ago

Stellantis 2024 Salesforce Supplier Breach: Lessons on Third-Party SaaS Risk

In June 2024, automaker Stellantis confirmed that a cybersecurity incident impacted some of its North American customers after attackers compromised a third-party service provider’s platform integrated with their Salesforce infrastructure. The breach exposed sensitive customer data, though financial and highly confidential information reportedly remained secure. The attackers exploited weaknesses in the external vendor’s environment to gain unauthorized access, demonstrating the risks inherent in today's interconnected supply chains. Stellantis responded by notifying affected customers, engaging security experts, and working closely with the vendor to contain and investigate the incident. This breach highlights the ongoing surge of supply chain and third-party risks as enterprises rely on hosted platforms like Salesforce for mission-critical operations. The event underscores the increasing sophistication of attackers targeting SaaS ecosystems and underscores the need for robust supplier security controls and monitoring.

High impact

Kill Chain

ICInitial Compromise(medium)
PEPrivilege Escalation(low)
LMLateral Movement(low)
C&CCommand & Control(low)
EExfiltration(medium)
IImpact(high)
Read report
Ransomware Attack Disrupts Major European Airports via Collins Aerospace in 2025
Airlines/Aviation9 months ago

Ransomware Attack Disrupts Major European Airports via Collins Aerospace in 2025

In September 2025, a major ransomware attack on Collins Aerospace, a critical provider of check-in and boarding systems, triggered widespread disruptions at several major European airports, including Heathrow, Brussels, and Berlin Brandenburg. The hackers targeted the Multi-User System Environment (MUSE) platform, which airlines rely on to coordinate check-in desks and gate assignments. As a result, more than 100 flights were delayed or cancelled, and thousands of passengers faced manual check-in procedures while airports scrambled to contain the operational fallout. Law enforcement and cybersecurity agencies are actively investigating, prioritizing the restoration of affected systems and mitigation of further impact. This incident underlines the escalating risk posed by ransomware targeting supply chain infrastructure and the aviation sector’s reliance on shared IT systems. It also reflects a broader trend of cybercriminals exploiting third-party service dependencies, bringing renewed urgency to layered defense strategies and zero-trust adoption for business-critical environments.

High impact

Kill Chain

ICInitial Compromise(medium)
PEPrivilege Escalation(low)
LMLateral Movement(medium)
C&CCommand & Control(low)
EExfiltration(low)
IImpact(high)
Read report
Microsoft Entra ID Flaw Exposed: How One Vulnerability Enabled Global Admin Impersonation
Financial Services9 months ago

Microsoft Entra ID Flaw Exposed: How One Vulnerability Enabled Global Admin Impersonation

In September 2025, Microsoft disclosed a severe security flaw (CVE-2025-55241) affecting its Entra ID (formerly Azure Active Directory) service. The vulnerability, which received a maximum CVSS score of 10.0, allowed threat actors to bypass token validation and impersonate any user—including Global Administrators—across any tenant. Successful exploitation could grant attackers unrestricted access to sensitive data and resources within affected organizations, making this a high-impact privilege escalation incident. Microsoft responded swiftly, issuing a critical patch to contain the risk and urging immediate customer action. This incident highlights the ongoing trend of identity-based attacks against cloud platforms, emphasizing the necessity of robust access controls and vigilant monitoring. The discovery reinforces the risks of SaaS/IDaaS privilege escalation, as attackers increasingly target provider-side weaknesses to achieve large-scale compromise.

Low impact

Kill Chain

ICInitial Compromise(high)
PEPrivilege Escalation(high)
LMLateral Movement(medium)
C&CCommand & Control(medium)
EExfiltration(low)
IImpact(low)
Read report
Multi-Vector Cyberattack 2025: AI, Chrome 0-Day, DDR5 and npm Supply Chain Breach
Financial Services9 months ago

Multi-Vector Cyberattack 2025: AI, Chrome 0-Day, DDR5 and npm Supply Chain Breach

In September 2025, a multifaceted wave of cyber threats was observed, including a Chrome zero-day exploit, AI-generated hacking toolkits, active exposure of DDR5 memory vulnerability (Rowhammer-based bit-flip attacks), and a virulent npm worm targeting the software supply chain. Attackers leveraged 0-day browser exploits to execute malicious code, engineered advanced AI tools for automation, and deployed the npm worm to laterally move via package dependencies. The surge in attack sophistication resulted in unauthorized access, rapid lateral movement, and significant operational disruption for developers and enterprises globally. This incident underscores an urgent pivot in attacker tactics—combining classic and novel vulnerabilities across infrastructure, code, and memory. The simultaneous exploitation of multiple vectors signals a broader trend of adaptive threat landscapes, increasing regulatory scrutiny, and the need for rapid detection, cross-layer visibility, and agile patching cycles.

Medium impact

Kill Chain

ICInitial Compromise(medium)
PEPrivilege Escalation(medium)
LMLateral Movement(medium)
C&CCommand & Control(medium)
EExfiltration(medium)
IImpact(medium)
Read report
ComicForm and SectorJ149 Launch Formbook Infostealer Attacks in Eurasia (2025)
Financial Services9 months ago

ComicForm and SectorJ149 Launch Formbook Infostealer Attacks in Eurasia (2025)

In April 2025, a previously unknown threat group known as ComicForm, in tandem with the SectorJ149 collective, launched a sophisticated phishing campaign against organizations in Belarus, Kazakhstan, and Russia. Exploiting spear-phishing emails, the attackers delivered Formbook malware, an advanced infostealer, to infiltrate sectors including industrial, financial, biotechnology, research, tourism, and trade. The campaign's attack chain leveraged malicious email attachments and deceptive lures aimed at harvesting sensitive credentials, exfiltrating business information, and enabling internal lateral movement, causing operational disruptions and exposing confidential data. This incident exemplifies the rise of regionally targeted malware campaigns by emerging threat actors who combine phishing, credential theft, and infostealer malware. Current threat intelligence points to increased infostealer usage, especially in sectors with valuable intellectual property, necessitating enhanced vigilance and stronger defense-in-depth strategies.

Medium impact

Kill Chain

ICInitial Compromise(high)
PEPrivilege Escalation(medium)
LMLateral Movement(medium)
C&CCommand & Control(medium)
EExfiltration(high)
IImpact(medium)
Read report

Security Research & Insights

Security Research & Insights with human-led deep dives into campaigns and cloud-native TTPs

Market Perspectives

Market Perspectives offering expert commentary and select breach analysis from industry leaders

How CNSF Protects Cloud Workloads

Cloud attackers don’t rely on a single exploit — they rely on paths.

Once inside, attackers move laterally between workloads, establish command-and-control through egress paths, and exfiltrate data through legitimate cloud services — often before detection tools generate an alert. These paths exist because most security architectures enforce at centralized inspection points, not at every workload. The paths that matter most are the ones that never reach a central firewall.

Aviatrix Cloud Native Security Fabric (CNSF) contains attacks by enforcing policy at every workload communication path — containing blast radius, blocking lateral movement, and cutting off egress before data leaves the environment.

Utilize the Network Layer

With CNSF, enterprises can:

  • Contain attack paths at runtime

    Gain visibility into east-west and egress workload communication and apply controls that limit lateral movement, unauthorized egress, and uncontrolled trust expansion.

  • Eliminate blind spots in workload-to-workload traffic

    Observe traffic across VPCs/VNets, regions, and cloud providers using cloud native telemetry — including paths that posture tools and point controls don’t model.

  • Secure modern and AI-driven workloads

    Understand how agents, services, and workloads communicate at runtime, and enforce policy to reduce the risk of misuse, over-privileged access, or unintended data flows.

  • Apply consistent Zero Trust controls without slowing teams

    Enforce segmentation, egress control, and encryption centrally across clouds — without agents, application changes, or developer friction.

See Your Attack Paths. Close the Gaps with CNSF.

Blast radius starts where your enforcement stops.

Most security architectures enforce at centralized inspection points. Attackers move between workloads on paths that never reach those points — building blast radius invisibly until detection tools fire, often too late.

The Executive Assistant That Broke the Company Why Shadow AI is the New Cloud Crisis card image

Your assessment delivers:

  • The Aviatrix Workload Attack Path Assessment (WAPA) analyzes real workload communication using cloud native telemetry to uncover attack paths already present in your environment — and shows how Cloud Native Security Fabric (CNSF) can break those paths with runtime enforcement.

Containment Era Intelligence

The threat landscape has changed.
Has your question changed with it?

In March 2026, TeamPCP proved that detection-first architectures cannot contain attacks that move through trusted code, not around defenses. Today’s threat actors don’t break in — they log in, blend in, and expand silently. This command center tracks the evolving threat landscape and helps you measure your Blast Radius — the architectural metric that defines resilience in the Containment Era.

8
Tracked Campaigns
82%
Intrusions are malware-free
— CrowdStrike GTR 2026
29 min
Avg. eCrime breakout time
— CrowdStrike GTR 2026
27 sec
Fastest observed breakout
— CrowdStrike GTR 2026

This command center tracks 8 active campaigns and measures your Blast Radius: what an attacker can reach once inside your environment.

Contain the Blast Radius

See the attack paths already present in your environment — and where CNSF containment controls would break them.

Cta pattren Image